It’s no secret that cybercrime has been escalating dramatically since 2020. Worse yet, small to medium-sized businesses (SMBs) are bearing the brunt of a large percentage of these cyberattacks. While many large enterprise organizations already have chief information security officers (CISOs) to help them continuously adapt to these evolving cybersecurity threats, a majority of SMBs do not.
With this in mind, all companies should have a resource to help them accurately understand the risks they face and build a mature security program to keep their organization safe. Threat actors often pass by companies with foundational cybersecurity controls and attack those less prepared. But that doesn’t mean you have to pay a fortune to have access to this expert experience. In this blog, I’ll explain how fractional CISO services work and offer a few additional cost-effective cybersecurity options for your business to consider.
What Are Fractional CISO Services?
Many IT providers offer IT consulting services so that organizations can still access the specialized IT skills they need without bringing on another full-time, highly paid executive. A fractional Chief Information Security Officer (CISO) is sometimes referred to as a virtual CISO (vCISO). These IT consultants fill the need to have the necessary expertise available to the organization, without the large price tag associated with a full time hire. vCISOs meet with the organizations they serve regularly to develop a security program strategic roadmap, producing regular executive reports, including progress tracking and recommendations.
While a fractional chief information officer (CIO) might be tasked with helping an organization increase productivity, gaining a competitive advantage through the use of technology, or handling the unique challenges associated periods of high growth or mergers and acquisitions, a fractional CISO will be able to help an organization accomplish goals related to security program development, regulation, and compliance.
Some common examples include:
- Implementing industry-specific compliance and regulatory controls
- Perform vendor due diligence and risk assessment
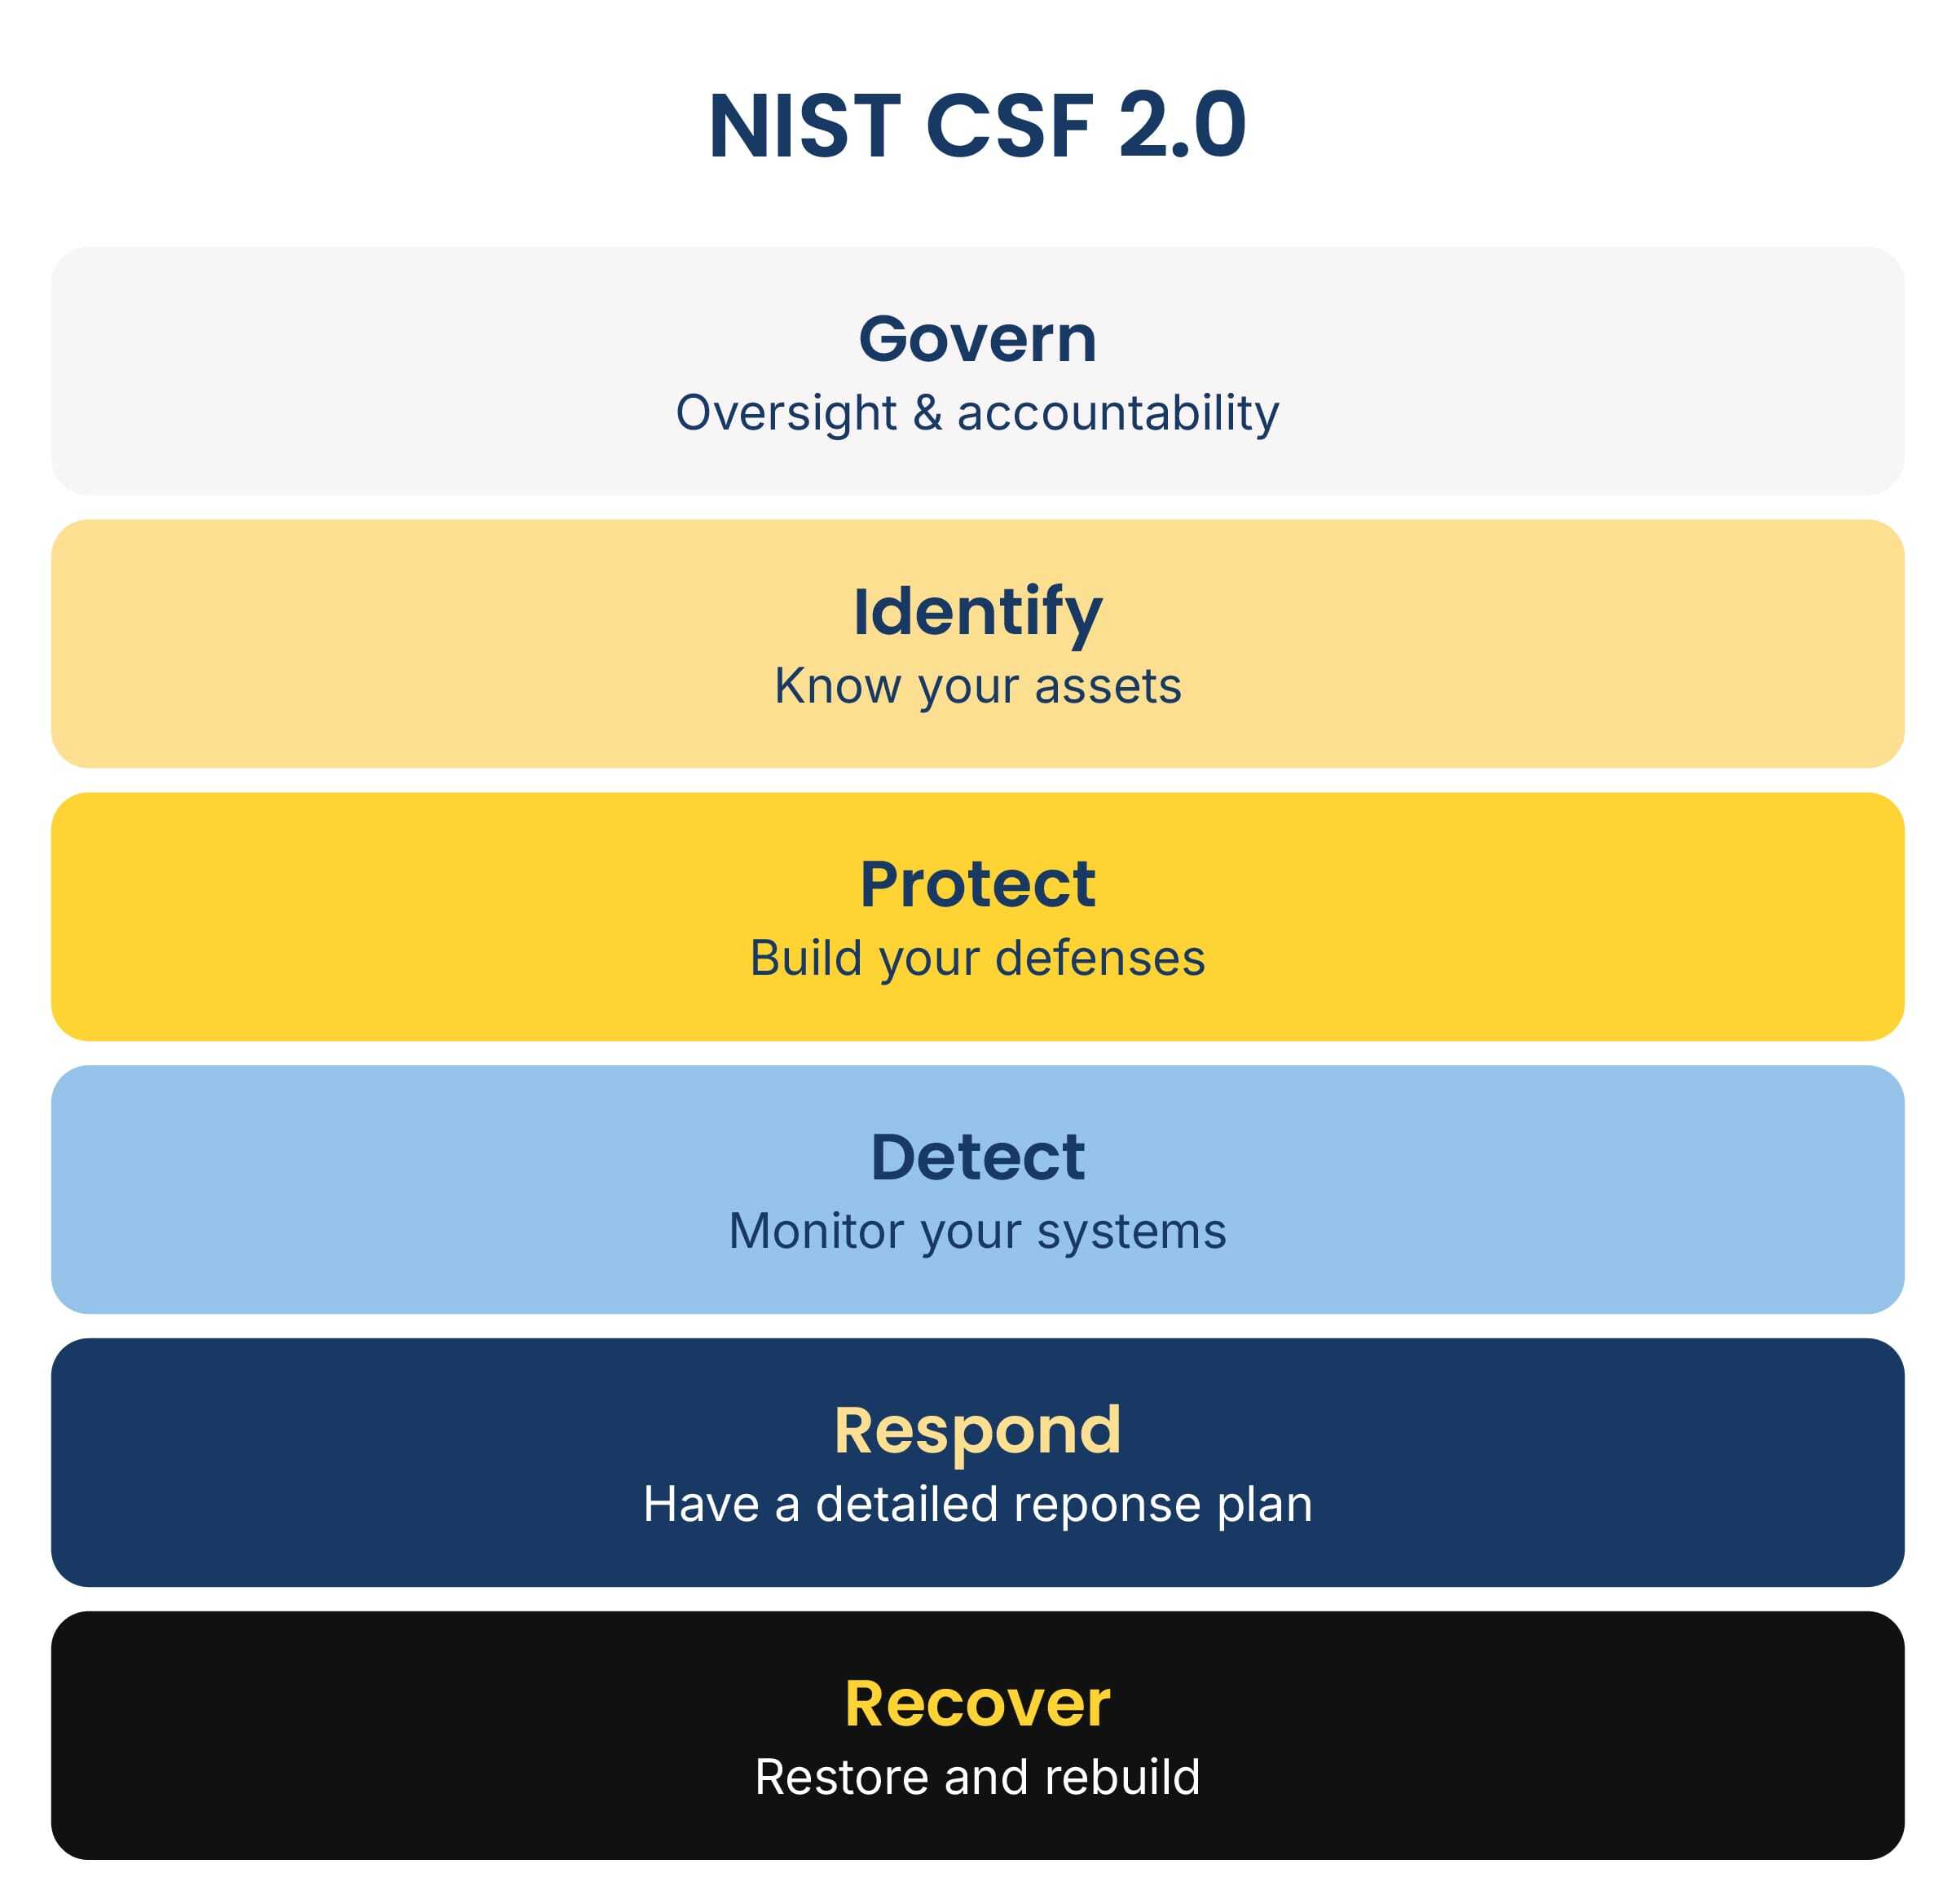
- Align your cybersecurity posture with best practices outlined in the NIST Cybersecurity Framework
- Minimize your organization’s risk of common cyberattacks
- Improve your security monitoring, detection, and response capabilities
- Build a culture of security
- Protect your intellectual property and other business assets
5 Benefits of Fractional CISOs

There are many additional benefits of having a fractional CISO working with your organization. Some of the most common advantages are:
1. You’ll Get More Cost-Effective Cybersecurity Solutions
With these services, smaller organizations that are now faced with preventing cyberattacks from hackers all over the world can access the same skills that have protected their much larger counterparts for a fraction of the cost.
2. Up-to-Date Cybersecurity Risk Management Is What They Do
Business technology changes by the year, but the cybersecurity landscape evolves much quicker. Large shifts are always occurring. Every month there are new developments and new vulnerabilities are exposed daily. That’s simply too much for most internal teams to keep on top of. But a vCISO will be able to keep your organization aligned with current best practices. And if your company is in a highly regulated industry, they can also help your business make sure it’s aligned with evolving requirements.
3. Virtual CISO Consulting Can Scale Up or Down
Should you ever need more of your vCISO’s time, your services can scale up. And if you ever need help with a complex IT project, many providers — Marco included — will also offer discounts on additional consulting services as part of your vCISO package.
4. Outsourced CISO Services Bring an Outside Perspective
Similar to managed IT, an outsider’s perspective alone can be extraordinarily helpful. Many industries will have unique risks and challenges, and a fractional CISO with a diverse background will be able to better match your security strategy to your business’s largest vulnerabilities.
5. They Can Dramatically Improve Security Awareness Training
Ultimately, when it comes to cybersecurity, a company’s employees are the first line of defense. Without proper training, they can easily become the “weakest link” in the organization’s cyber defenses. Security awareness training can be remarkably effective, but it needs to be engaging and relevant. What’s more, when it comes to security, employees often follow suit with the behavior they see modeled by their C-suite executives. Often times, a vCISO will conduct role specific and executive focused security awareness training that speaks directly to the business risks that these executives are concerned about in a way that relates better than more generalized training.
A vCISO can help you develop training materials that address real-world scenarios your employees are likely to encounter. And they will also have the standing to advocate for the necessary resources and support from executives. They can also help you conduct security tabletop exercises that allow your company to play out business critical thread scenarios in a safe way and make sure that your incident response plan is sufficient.
Other Options for Getting Help With Cybersecurity Framework Implementation

A fractional CISO certainly isn’t the only tool at your disposal when it comes to implementing cybersecurity best practices.
If you’re not sure whether your current posture is enough, we’ve actually put together a simple online quiz to help you find out. And if you already know your data is vulnerable, but if you’re not ready to bring on a vCISO, you might consider beginning your journey through a cybersecurity review of your environment. At Marco, our cybersecurity assessment has been a very popular option for many small to midsize businesses doing just that. It gives them a holisitc understanding of where they are currently at, and identifies any major gaps that they may have in their IT environment.
Companies of all sizes, across industries are affected by these cybersecurity issues. Threat actors are often targeting small-to-medium sized business because in many cases they do not have the foundational controls and solutions in place. Between ransomware, business operations being disrupted, or having your company’s reputation ruined by having your name in the headlines from an attack, it is important to take steps to mature your cybersecurity posture and decrease your risk. Want to learn more about if a vCISO is right for your organization? If you’d to do a deeper dive on this topic, click the link below to watch the recording in your own time!