Cyberattacks and IT incidents have risen sharply in 2025 and 2026, and if current trends are any indication, cybercriminals are becoming bolder and far more dangerous. Just this past January, hackers infiltrated Nacogdoches Memorial Hospital's network, stealing information from over 2.5 million patients. In just the first six months of 2026, more than 19 million individuals have been affected by healthcare data breaches reported to the U.S. Department of Health and Human Services Office for Civil Rights (OCR).
In response to the increase in the scope and severity of cybercrime, healthcare leaders and regulators are calling for stronger action. The OCR continues to emphasize that cybersecurity and patient privacy must be top priorities for all healthcare organizations — not just a compliance checkbox.
So in this guide, I'll explain what the OCR regulates, what it's demanding, what penalties look like, and where to start.
What is the Office for Civil Rights?
The Office for Civil Rights (OCR) falls under the jurisdiction of the U.S. Department of Health and Human Services and is tasked with enforcing the Health Insurance Portability and Accountability Act (HIPAA), the Patient Safety Act and Rule, as well as Privacy, Security, and Breach Notification Rules.
Is your organization regulated by HIPAA?
Before diving into what the OCR demands, you need to know if you're subject to its enforcement. Most organizations reading this will already know if HIPAA applies to them, but for those that don't, there are two main types of organizations subject to HIPAA: covered entities and their business associates.
Covered entities
Covered entities include:
- Hospitals and medical centers
- Physician and dental practices
- Clinics and urgent care centers
- Mental health and behavioral health facilities
- Substance abuse treatment centers
- Nursing homes and long-term care facilities
- Home health agencies and hospices
- Ambulatory surgery centers
- Medical laboratories and diagnostic centers
- Pharmacies
- Vision care centers and optometry practices
- Physical therapy and rehabilitation centers
- Telehealth providers
Business associates
This group is much more broad and can be thought of as the downstream contractors and vendors of covered entities. While covered entities' requirements are explicitly identified in law, business associates are bound to protecting ePHI through the use of contracts called Business Associate Agreements (BAAs). If you are a contractor or subcontractor for a covered entity that requires access to protected health information, this is you.
If either of these applies to your organization, the OCR is watching — and its enforcement is intensifying.
Core HIPAA requirements the OCR is focused on
HIPAA's requirements haven't changed, but 2026 breach data proves why the OCR prioritizes them so heavily. Here's what organizations must do:
Know what you have
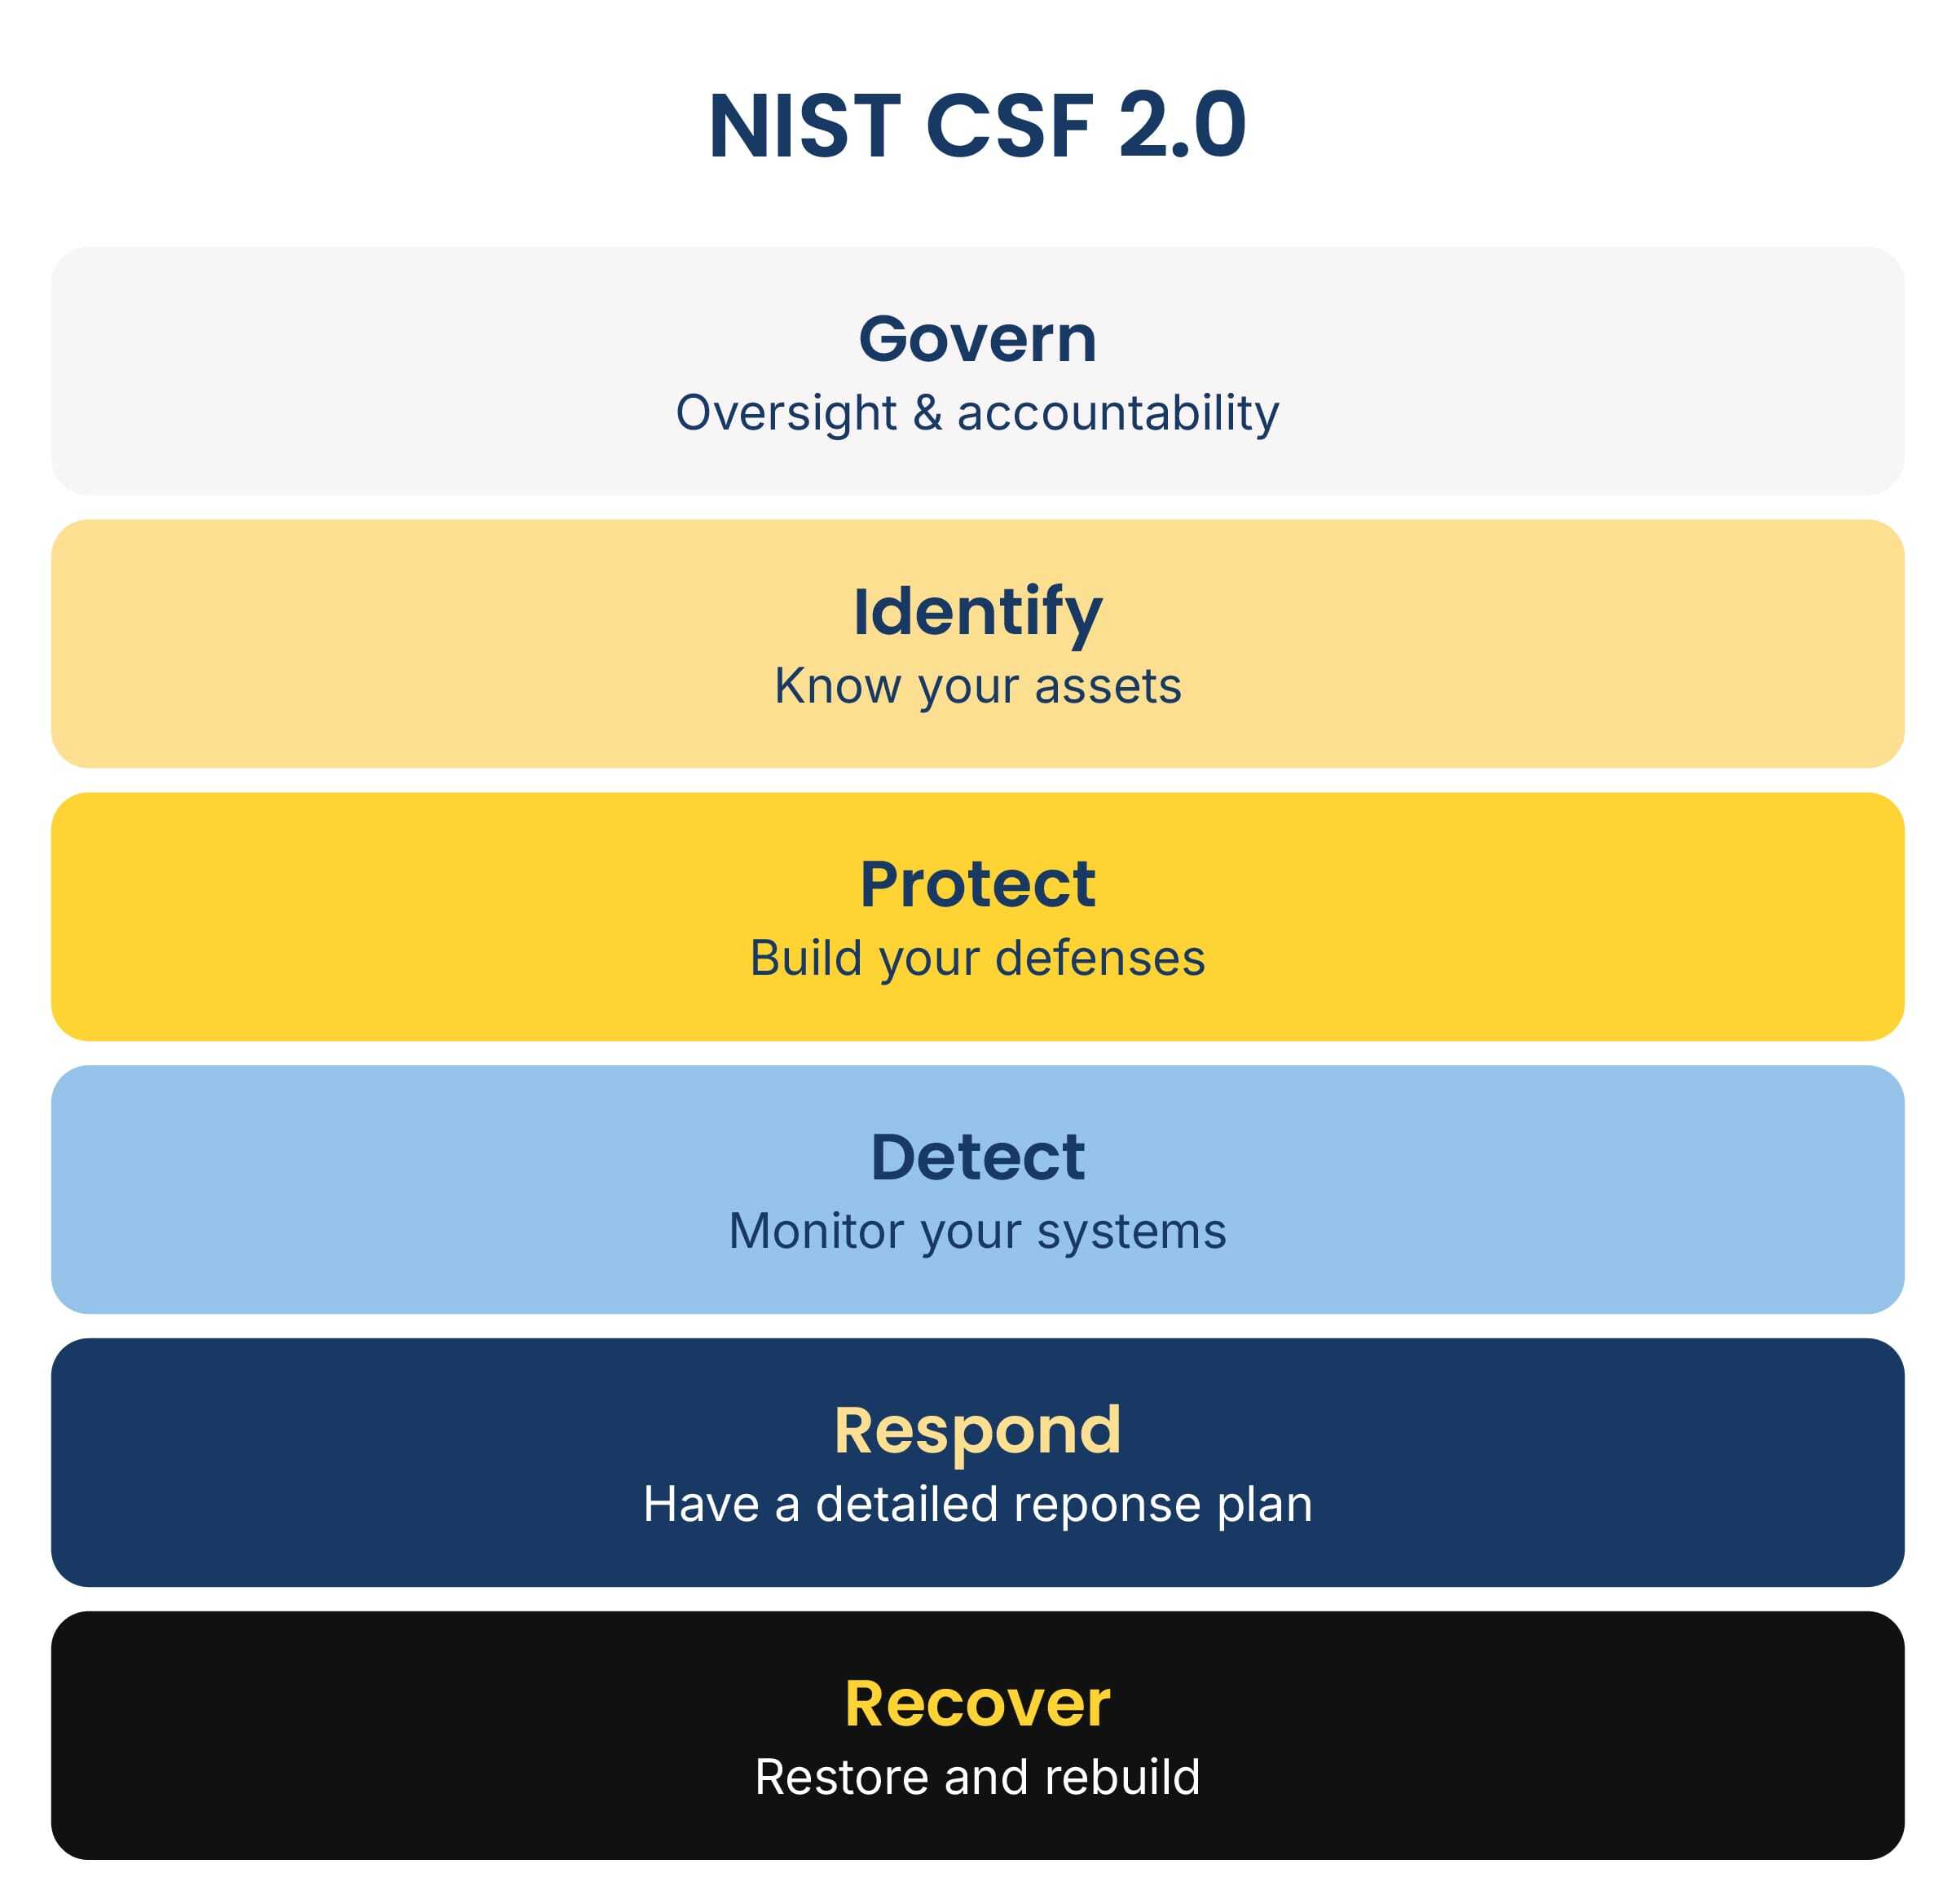
Conduct a formal risk analysis to inventory all systems, devices, and data flows that handle patient information. The Nacogdoches breach happened, in part, because the organization didn't have complete visibility into what was connected to their network. You can't protect what you don't know exists.
Secure it properly
Strong authentication and access controls are non-negotiable. Implement multi-factor authentication where possible. Encrypt data both in transit and at rest. Maintain offline, encrypted backups of critical data — and test those backups regularly to ensure they're actually recoverable when you need them.
Stay vigilant
Patch and update software and operating systems quickly. Conduct regular vulnerability scans to identify weaknesses before attackers do. Review system activity and audit logs to catch unauthorized access. The OCR expects ongoing monitoring, not a one-time assessment.
Prepare your people and your response
Security awareness training is mandatory, not optional. Your staff is your first line of defense. Equally important: develop and document a plan for responding to breaches. When an incident occurs — and statistically, it will — your response speed and thoroughness determine the damage.
HIPAA compliance penalties to keep in mind
The OCR has been cracking down on HIPAA violations as part of its mission to safeguard patient data. Regardless of whether a violation is deliberate or accidental, the penalties can be severe, including stiff fines and jail time, depending on the circumstances of the violation.
In 2024, one healthcare organization entered into a $1.3 million settlement with the OCR after repeatedly failing to protect sensitive data. These aren't isolated incidents. With more than 19 million individuals affected by breaches in 2026 alone, the pattern is clear: Organizations without documented, mature security practices are at risk, both operationally and legally.
Of course, it's easy to focus on penalties when discussing HIPAA. However, providers stand to lose much more than money if there is a data breach; they could also lose patient trust. Patients who don't believe their data is secure may withhold vital information from their health care provider, which may, in turn, affect their quality of care.
Frequently asked questions
Get additional information about how healthcare is targeted, and what they can do to protect themselves.
What's the most common type of healthcare data breach?
Hacking and IT incidents dominate, accounting for 173 of 189 reported breaches in 2026 so far. This includes unauthorized network access, ransomware attacks, and exploits of unpatched systems.
Why do cybercriminals specifically target healthcare organizations?
Healthcare data is valuable because it contains everything a criminal needs: medical history, insurance information, Social Security numbers, and financial account details.
A single healthcare record can sell for 10–50 times the price of a stolen credit card number. Additionally, healthcare systems often can't shut down for emergency response. A ransomware attack on a hospital creates leverage — pay up, or patient care suffers and lives are at risk.
What's the difference between a healthcare data breach and a cybersecurity incident?
A cybersecurity incident is any unauthorized access to a system. A breach is when that incident results in access to protected health information (PHI) that puts individuals at risk. Not every incident becomes a breach; some are caught and contained before data is compromised. But once PHI is exposed, you're legally obligated to notify affected individuals and the OCR.
What does HIPAA compliance actually require?
HIPAA requires a documented risk analysis, security awareness training, access controls, encryption of data in transit and at rest, audit controls, and a plan to respond to breaches. The OCR has been cracking down on organizations that have policies but no real security practices in place. Compliance isn't a checkbox — it's evidence of active, ongoing security management. A solid data security governance program ties these practices together and ensures they're enforced consistently across your organization.
What happens if your organization fails HIPAA compliance?
Penalties range from $100 to $50,000 per violation, and violations can stack. But the real cost isn't always financial. A breach can destroy patient trust, disrupt operations, and damage your reputation for years. Consider also the operational impact: When a hospital's network goes down due to a ransomware attack, patients can't access their records, labs can't process tests, and emergency rooms may need to divert incoming patients. A documented cyber incident response plan helps your team move faster and more decisively when something goes wrong.
Who needs to comply with HIPAA?
Covered entities (i.e., hospitals, clinics, medical practices, pharmacies, nursing homes) and their business associates (i.e., billing companies, IT vendors, cloud providers, consultants). If you electronically transmit protected health information, you're regulated.
Getting a quick, complimentary cyber check-up
The 2026 breach data is clear: Healthcare organizations that act on cybersecurity now are the ones that avoid becoming statistics later.
But the first step doesn't have to be time-consuming or expensive. Our cybersecurity team put their heads together to create an online cyber health tool that can identify common gaps and deliver tailored recommendations on where your organization should focus first.