In 1999 Congress passed the Gramm-Leach-Billey Act (GBLA) to protect consumer privacy and financial data and outlaw deceptive practices. The act has three sections: the Financial Privacy Rule, the Safeguard Rule, and the Pretexting Rule, and it applies to any institution that offers financial services.
Released in 2002 and taking effect in 2003, the FTC also issued an additional rule — the Standards for Safeguarding Customer Information, which sets standards for financial institutions to follow when implementing these safeguards.
What’s the Scoop on the Safeguards Rule?
The Safeguards Rule gives the FTC more power to regulate financing wherever it is offered and requires that organizations maintain proper information security to prevent unauthorized access or disclosure of consumers’ personal information.
Cybersecurity has come quite a long way since the initial passing of this legislation. The act was purposefully vague in terms of compliance, allowing the newly empowered FTC (as well as other federal agencies) to respond to changes, including the dramatic increase in cyberattacks. The FTC is also at liberty to specify what organizations should do to maintain compliance over time.
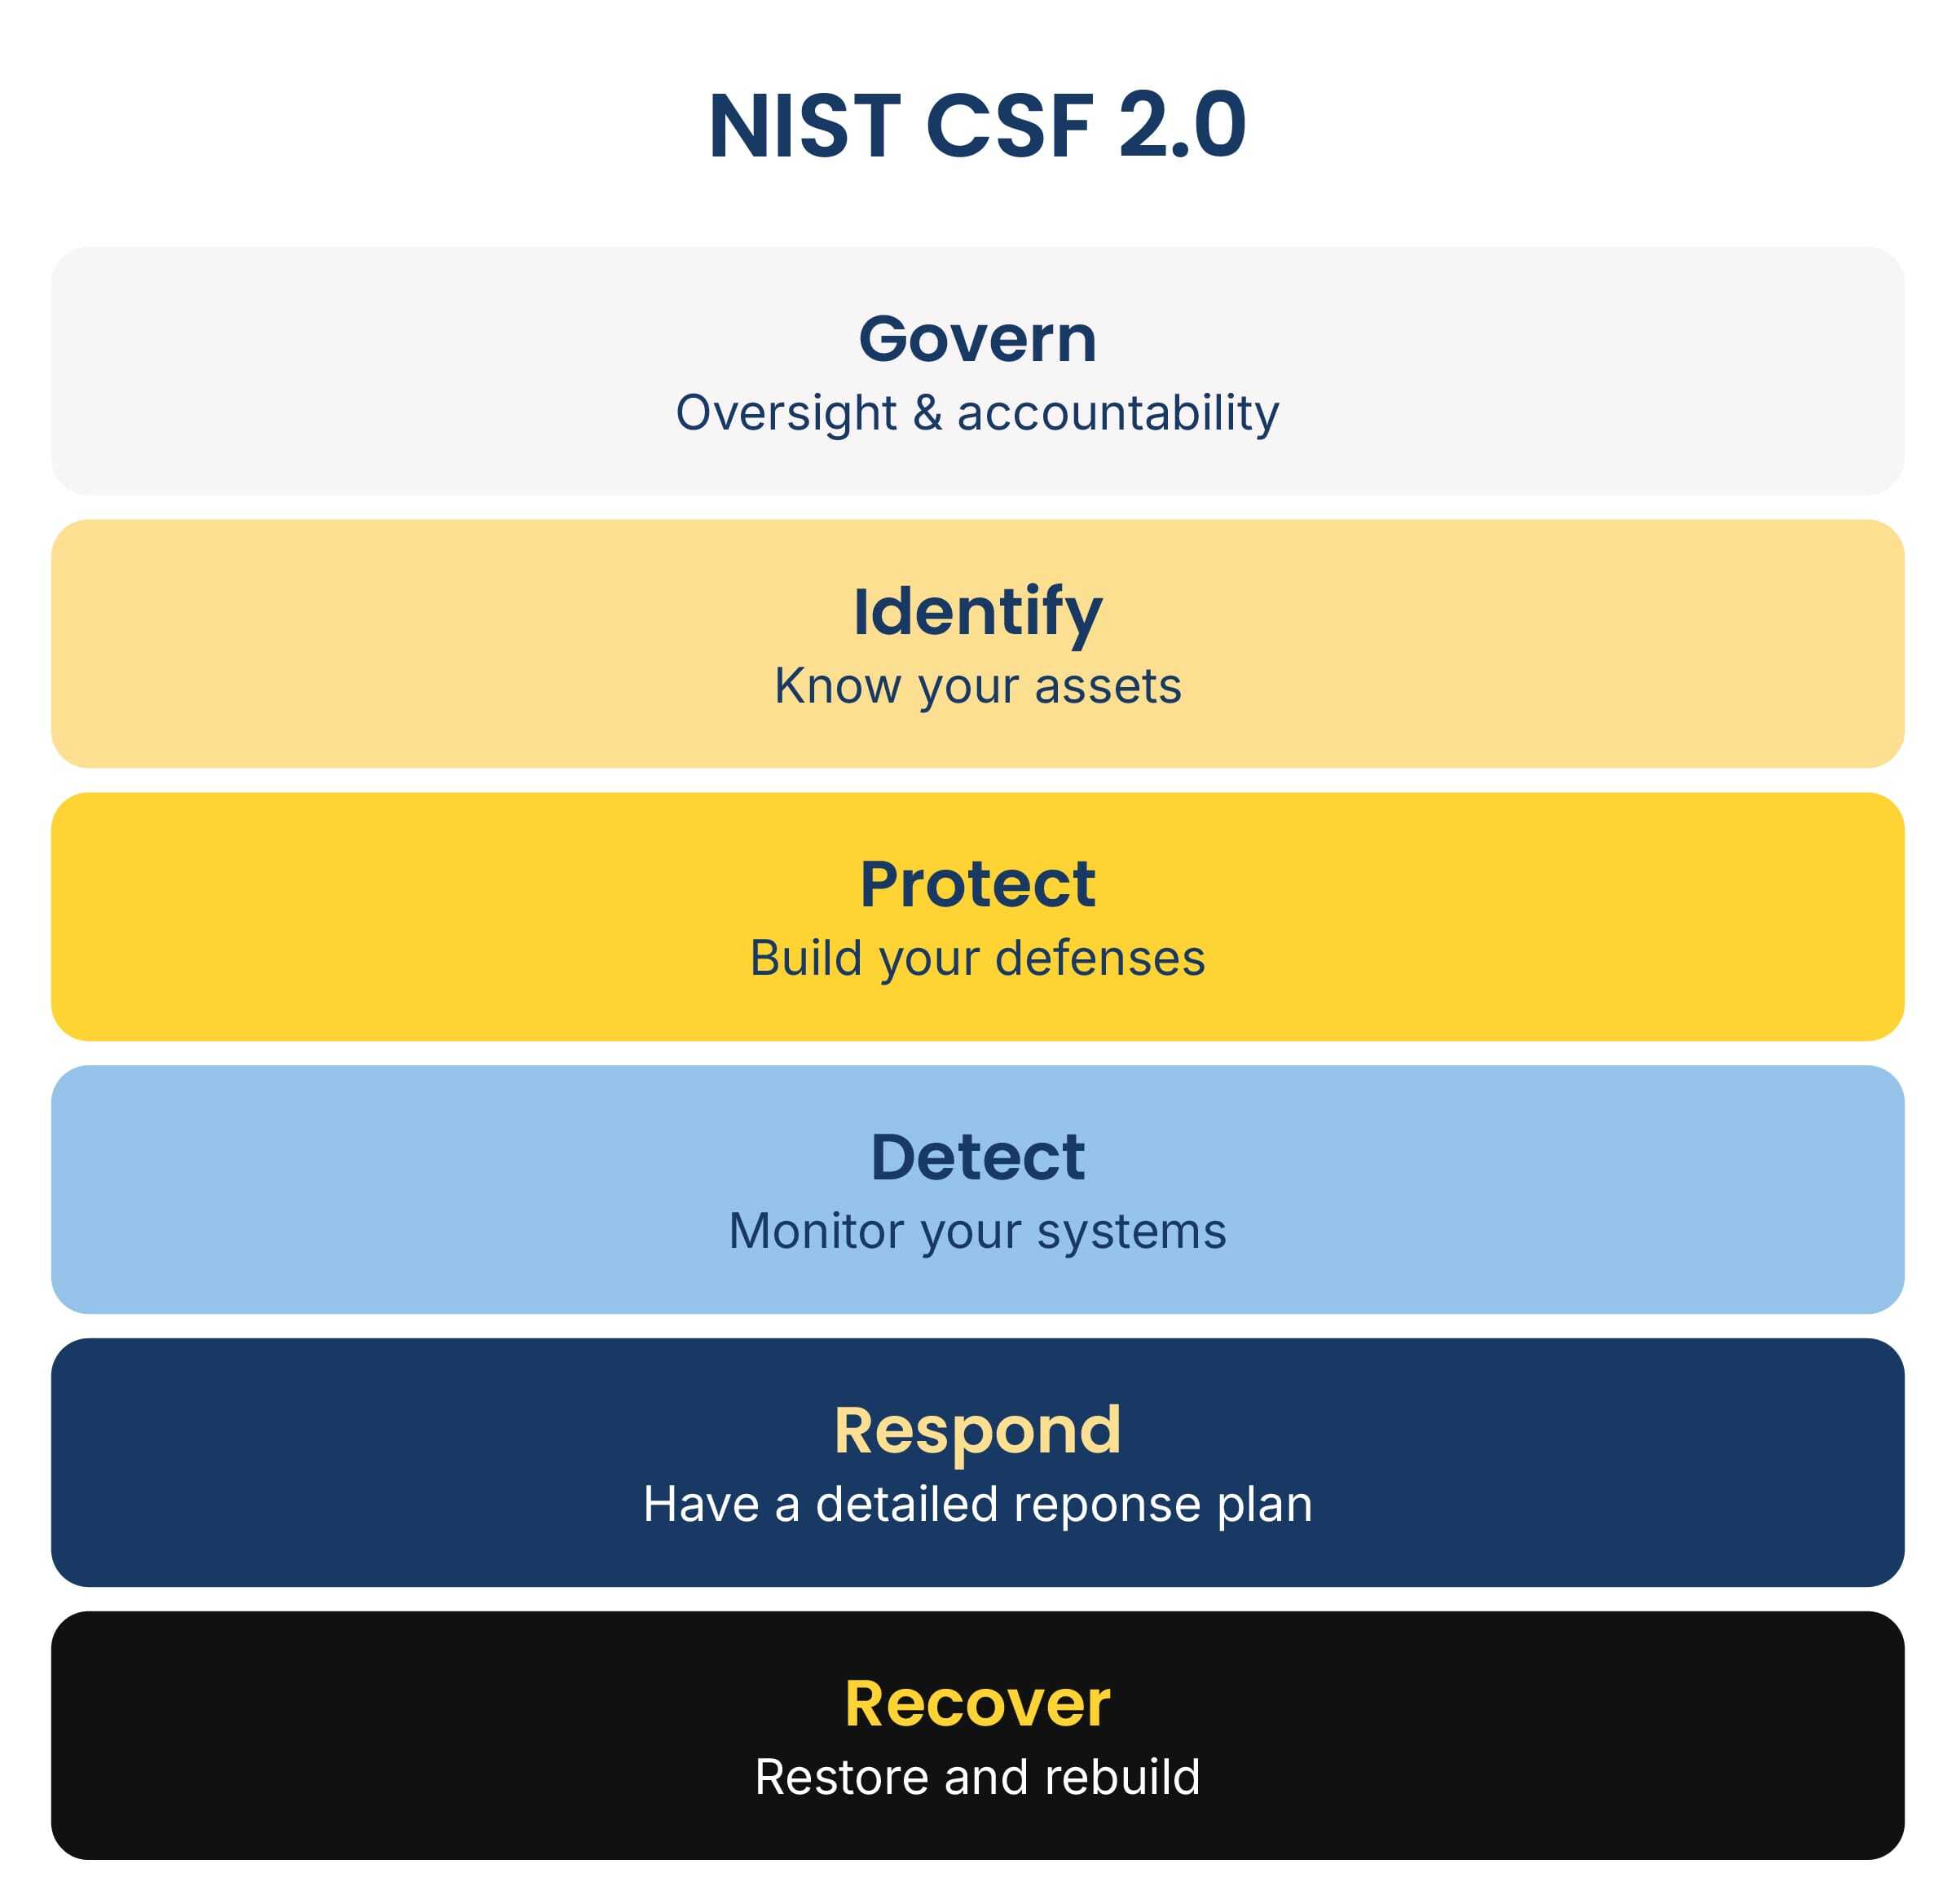
For those just jumping into this topic, this blog from the FTC is a plain English summation of best practices called out in every framework or standard worth its salt. It walks organizations through nine straightforward elements of what it takes to build a reasonable information security program.
What Industries Are Affected?
This revised Safeguards Rule more explicitly addresses non-banking financial institutions such as mortgage brokers, motor vehicle dealers, law offices, accounting firms, and other businesses that have such customer information. This expanded group of industries is required to develop, implement, and maintain a comprehensive security program to keep their customers’ information safe.If you’re in any of the following industries, you are required to comply with the Safeguards Rule:
- Car dealerships
- Car rental companies
- ATM operators
- Couriers
- Credit monitoring companies
- Debt collectors
- Mortgage and payday lenders
- Property appraisers
- Real estate firms
- Retailers
- Tax preparers
- Higher education
You Read That Right — the FTC Affects Auto Dealerships Too
Let’s take one of our customer segments, auto dealerships, as an example. While I’ve yet to meet an organization that loves having to meet compliance, these updated requirements are long overdue in this industry.
According to a Total Dealer Compliance study, 84% of consumers say they will not buy another car from a dealership that has been careless with their data. While many small to midsize businesses still suffer from the illusion that they’re too small for hackers to target, one major cybersecurity incident could cost them their entire business. It’s just not worth it.
No regulatory enforcement agency takes joy in watching businesses get hacked. But that is exactly what’s happening on an increasingly frequent basis. And while Marco is always there to help recover, we’d all prefer to do everything in our power to protect your data before something bad happens, including regulatory fines.
Did I Mention Fines Yet?
Failure to meet a compliance deadline can result in a penalty of $46,517 per violation. For many small organizations, that can eclipse the year-one cost of actual compliance with the security requirements. You know, those requirements that provide significant benefits to protecting the organization and its customers’ data.
And don’t forget that regulatory penalties are only one price you may pay for poor cybersecurity hygiene. Your reputation? Shattered. Potential civil judgments from an actual breach? Expensive. The list continues, but we’ll move on.
What Are Those Deadlines?
Back in October 2021, the FTC announced changes to the Safeguards Rule that would have required compliance for these previously unenforced industries by December 9, 2022.
For those late to the party looking for a silver lining, certain provisions of the updated rule were extended on November 15, 2022, to June 9, 2023. A six-month extension may feel like a long time today, but as the past 12 months have demonstrated, that deadline will be here before you know it.
As your trusted technology provider, Marco’s dedicated Cybersecurity Consulting Division is standing by to help you meet these new regulatory requirements, including multi-factor authentication.
Multi-Factor Authentication and Other New Requirements
Many specific additions have been added to the Safeguard rule outside of just who is now considered “in scope” for enforcement. There are new policies, reports, documentation, training, and technical requirements.
The technical requirement additions include the following:- Multi-Factor Authentication (MFA)
- Penetration Testing and Vulnerability Assessments
- Monitoring and Logging Solutions
These requirements should come as no surprise. For example, according to the national security cyber chief, MFA can thwart 80–90% of cyber-attacks. The bad news? Only 26% of US-based companies use it.
By the way, have I mentioned that Marco offers a number of multi-factor authentication solutions, including Cisco Duo and Microsoft Azure AD? And that we have in-house experts ready to ensure it is implemented, configured, and operating effectively. I haven’t? Weird. I usually do by this point. Anyway…
Take Me to Your Leader.
Marco is here to help, and we speak business owner, executive blather, and manager-ese. Regardless of where you are in your FTC Safeguard Rule journey, we are standing by. (Well, not literally. But we are very passionate about this topic, so we’d appreciate a call!)
If you think your business may be affected by the FTC’s updated rule, ask your Marco representative to learn more about our FTC/GLBA Security and Compliance Consulting Services.
For those unaffected by the rule, and who may be still reading this (Which…this is what you do for fun?), a comprehensive Cybersecurity Assessment from Marco is the perfect place to start, mature, or otherwise validate your security posture so you can make informed, objective decisions.