The world of cybersecurity is always changing; new vulnerabilities and threat actors seem to pop up overnight — well-armed and motivated. If you've been reading the headlines about the recent mother of all breaches (MOAB) release on the dark web, it's a stark reminder that we must always remain vigilant.
In this blog, I’ll break down the situation and offer some tips for businesses looking to better protect themselves and their customers.
So What Exactly Happened?
In late January of 2024, it was announced that a massive data leak was discovered on the dark web, which included over 26 billion records and took up over 12 terabytes of data. It was almost instantly referred to as “the mother of all breaches” because of the staggering size of the data.
Why You Shouldn't Panic
Much of the discovered data was already known to have been compromised from previous incidents, including major platforms such as LinkedIn, Tencent, and Twitter, amongst others.
Why You Should Be Cautious
SpyCloud, a cybercrime analytics and prevention company, recently announced that roughly 1.6 billion records “appeared distinct.” This means that in addition to data being previously available through past data breaches, some new data was included as well.
How To Protect Yourself and Your Business
The average cost of a data breach was $4.45 million in 2023, the highest average on record. Yes, it’s that bad. But the vast majority of data breaches are entirely preventable. So don’t use this data breach as an excuse to throw up your hands. Use it as a reminder to get smart about cybersecurity.
Review Cybersecurity Best Practices
If you haven’t upped your cybersecurity posture in the past few years, now’s your wake-up call. Make the time to review your basic cybersecurity posture and ensure that common controls are in place. With all this data being compiled in one place, it makes it even easier for even the most basic malicious hackers to attack your accounts with any credentials available from previous breaches.
Follow basic cybersecurity hygiene. For starters, make sure your staff isn’t guilty of any of these:
- Using passwords that have been involved in past breaches
- Not using MFA on all accounts, including VPN, cloud accounts, and admin accounts
- Re-using passwords
Watch for Phishing Attempts
Be on high alert for phishing emails that may be tailored to their target — you!
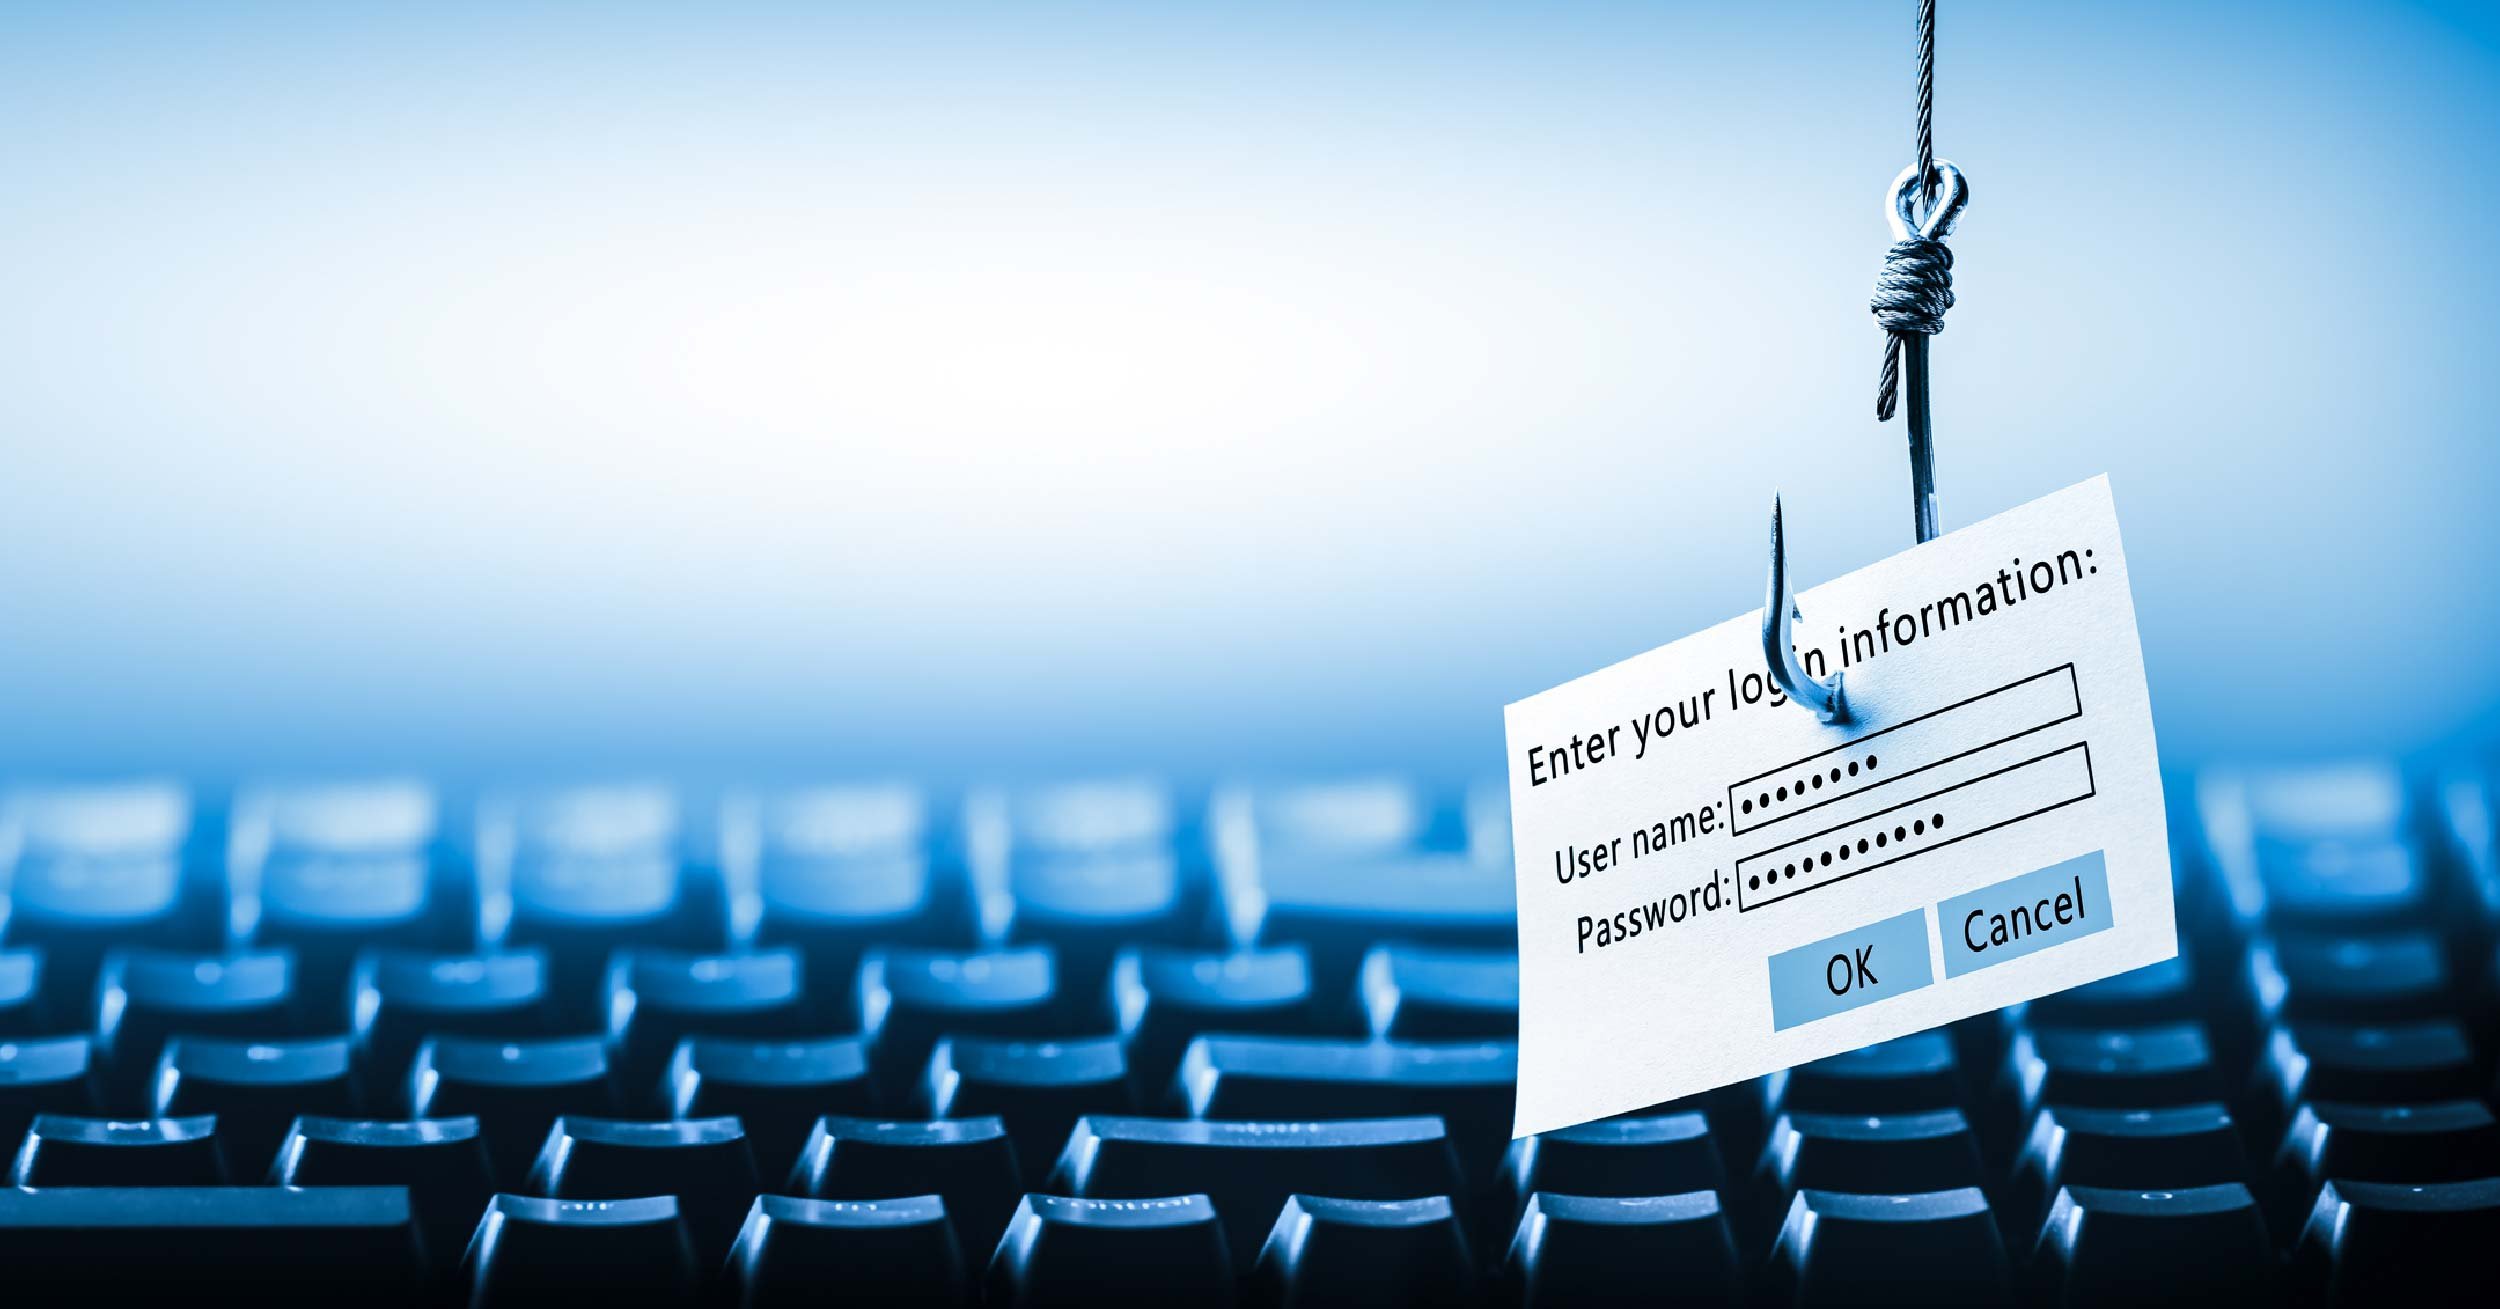
With this compromised data out there, attackers will have more accurate information about individual accounts that were involved in these breaches. Attackers can and often do use templates to trick you into thinking it is from the actual vendor, so make sure you click on known secure links and bookmarks, search results, or go directly to a company's homepage.
Don’t assume that you’re too smart to fall for a phishing scam. Hackers have been upping their game to use your brain’s cognitive biases against you — including overconfidence.
Monitor for Compromises
There are many tools out there to monitor to see if your data has been included in data breaches. Perhaps the easiest place to start monitoring this is to go to www.haveibeenpwned.com, enter your email address, and review your results.
Getting Up To Speed on Cybersecurity
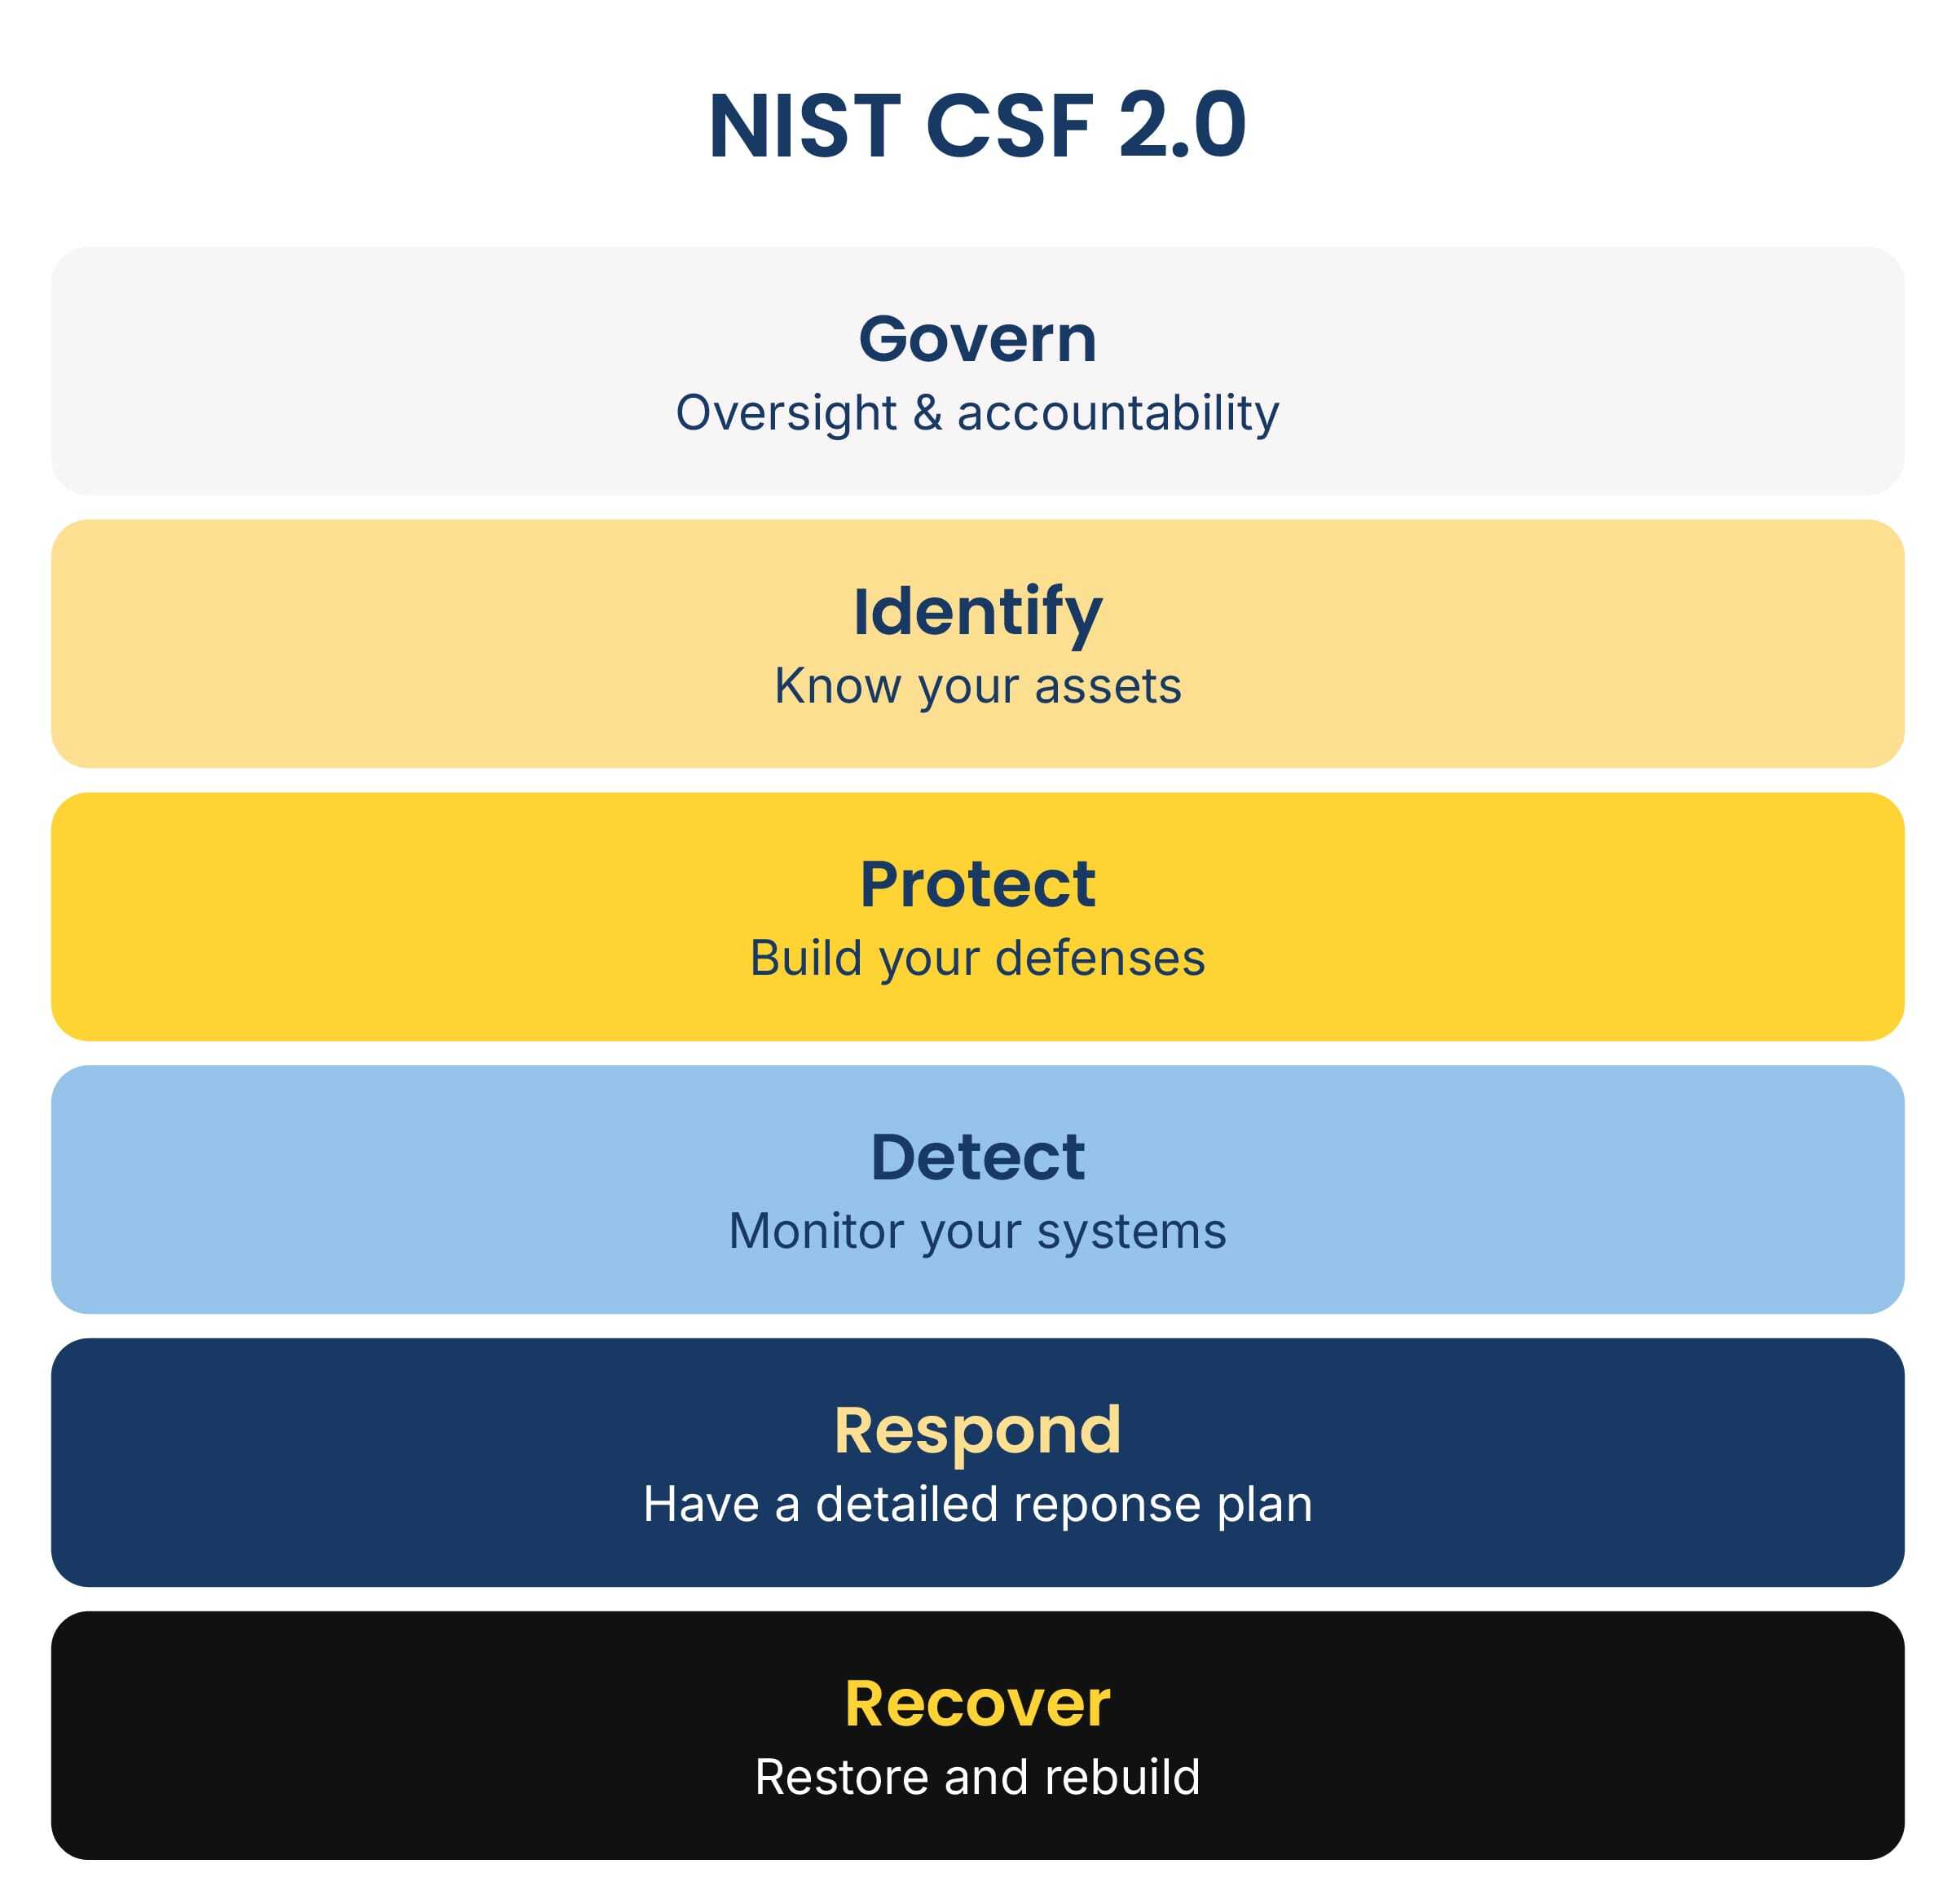
Cybersecurity evolves quickly, and it’s becoming a specialized field. Many internal IT teams simply don’t have the time or the resources to keep on top of this. So we’ve put together a cybersecurity checklist to help simplify the recommendations of the National Institute of Standards and Technology’s Cybersecurity Framework (NIST CSF).
Pro tip: You can also use this checklist to make sure your current IT provider is taking good care of you. Just like in every business, not all providers are the same, and some have been known to cut corners.
But if you can check off all of the boxes, congratulations! You’re in good shape, and you should have some peace of mind right now! If you can’t, then at least you’ll know exactly where your vulnerabilities are and how to address them.