"We've noticed suspicious withdrawals from your account. Click this link immediately to verify your information, or your account will be suspended."
Would you ever fall for this common phishing technique, or perhaps another one like it? According to Avast, 61% of Americans are highly vulnerable to phishing emails. Six out of ten is pretty high. You might be tempted to dismiss that figure; after all, you aren't that easily tricked. Unfortunately, that's a fairly common response and one that tends to get people into trouble.
Social scientists are beginning to focus more attention on this area of cybersecurity, and are finding that most people tend to be overconfident, and believe that only the foolish fall for email scams. After all, we've all been warned about the "Nigerian Prince" or 419 scam, and older scams like these tend to be more obvious. That said, they work more often than you'd think. Every year, that scam still pulls in about $700,000.
Still, you're not going to fall for something like that...are you? Don't be so quick to say no. It isn't always easy to spot a phish, and the more overconfident you tend to be, the easier it is to let your guard down.
Let's explore what phishing actually is, and why phishing training is such an important pillar of cybersecurity.
What Is Phishing?
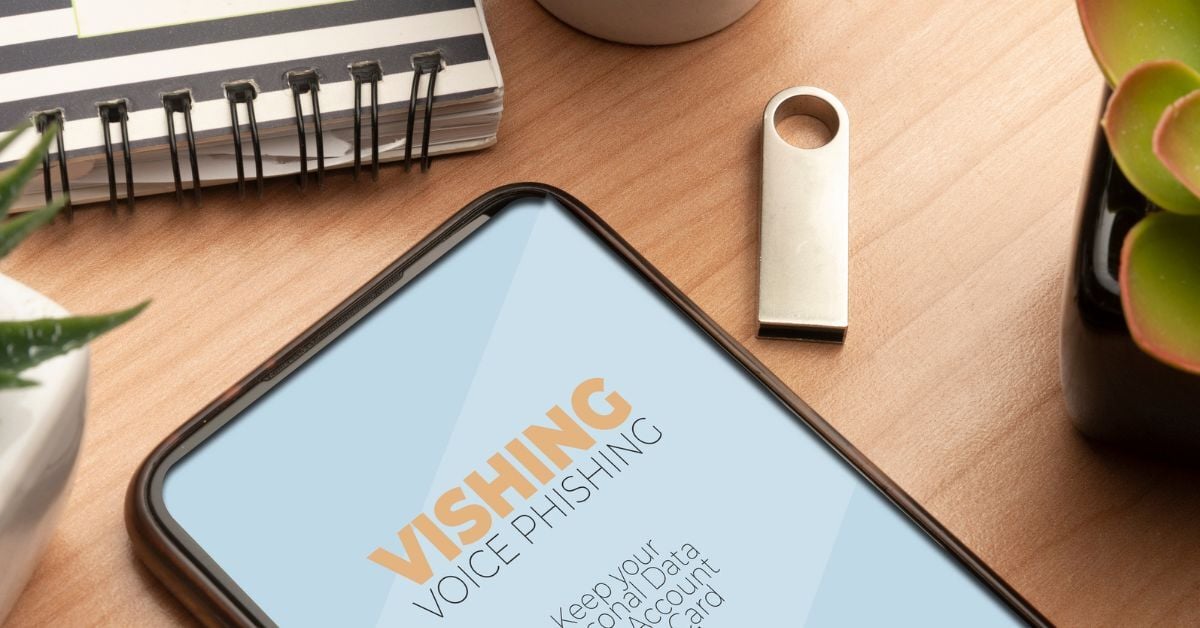
 Phishing is the act of trying to trick someone into revealing personal information, like login credentials, credit card numbers and more. Phishing scams are commonly sent through email and text, but these types of scams can also be carried out by phone. Phishing by phone is commonly referred to as vishing.
4 Common Misconceptions About Phishing
I've already highlighted the most dangerous misconception people have about phishing, which is that they’re too smart to fall for it. But there are others that are equally important to dispel:
1. Phishing Isn't A Big Cybersecurity Threat
Many employees assume that their company's data is well protected due to its many other cybersecurity strategies. But what they don't understand is that cybersecurity is not dissimilar to securing more tangible property. The best lock in the world doesn’t do anything if you, in essence, hand criminals the keys. Login credentials are the keys to your business’s network, and that’s exactly what employees are handing over in many phishing schemes. Not surprisingly, most breaches happen due to human error.
They're also happening far more often and costing us a lot more. According to the State of Phish Report, phishing attacks are on the rise, and they're becoming more successful, with a year-over-year increase of more than 45%. On average, phishing costs American companies $14.8 million per year.
2. Phishing Emails Always Come From A Stranger
Many blogs warn about clicking on email links that are sent from addresses you don't recognize. That's still a good warning, but many phishing emails these days are designed to look like they're coming from a coworker, or could be, in fact, originating from your coworker's already-hacked account. Phishing emails are getting better at disguising themselves and may appear like they're coming from your own HR department, for example.
3. Phishing Is Obvious
Phishing emails can sometimes be obvious…if you're watching out for them, and know how to recognize the telltale signs. But when you're in a rush, it's natural to make careless mistakes now and then. Hackers know this, and try to take advantage of a distracted moment. That's why many hackers nowadays will send out their phishing emails on a Friday evening or over the weekend when you aren't as focused. Additionally, phishing emails often imply urgency to try to get you to respond quickly before you've had time to think.
4. Phishing Emails Always Contain Poor Grammar
It's still a great idea to be suspicious when an email that looks like it's coming from a trusted company contains obvious grammatical and spelling errors. However, the absence of these things does not mean you can let down your guard. Ransom attacks are a highly profitable business, and cybercriminals have invested more resources into making their attacks more sophisticated, including upgrading their grammar and spelling.
How Hackers Use Social Engineering To Bait Their Hooks
 While the old 419 scam is still alive and well (and profitable), more of us aren't falling for such obvious bait. So criminals have also gotten more sophisticated in how they will overcome your skepticism using social engineering. Social engineering attacks manipulate a potential victim's emotions in order to lure them into divulging sensitive data. For example, a socially engineered attack may try to arouse fear or even curiosity to trick someone into clicking a link or entering sensitive information.
A hacker may go even further, and try to use personal relationships and hierarchies in order to pressure employees to click on a link. For example, one phishing email was successful in targeting Coca-Cola employees because it was designed to look like it was from a legal executive, and asked the recipient to click on an important message from the CEO. More recently, hackers successfully imitated the U.S. Department of Labor and asked recipients to submit bids in order to steal their Microsoft 365 credentials.
Regular Training Is Important
Chances are that after reading this far, you’ve already gotten better at recognizing sophisticated phishing attacks, and you won't fall for an email that looks like any of these previous examples. But if you hadn't just read that last paragraph, would you have recognized those emails for what they are? How about the next round of phishing techniques, or the next? As cybercriminals become more creative, if one phishing technique stops working, they'll just try another. Ongoing training is important to raise awareness about the increasing subtlety and sophistication of phishing schemes, and how damaging one careless click can be.
A Trusted Technology Partner Can Help
Marco's cybersecurity experts are constantly monitoring new and emerging threats, and adjusting their strategies accordingly. No security system on earth is completely impenetrable, and human error will always be the easiest access point. But our cybersecurity best practices can safeguard your valuable data, and make your organization a far less tempting target.