If your business hasn’t yet experienced a ransomware attack, but you aren’t actively preventing one, you’ve been very lucky. But luck has a way of running out.
I’m not saying that because I’m trying to scare you. I’m saying it because I hear so many small business owners say they think they’re too small to be a target. That’s unfortunately not the case, and you deserve to know the full truth about ransomware in 2023.
The FBI has reported a 62% year-over-year increase in ransomware attacks, and the average ransom demand is 2.82% of an organization’s total annual revenue. Perhaps that in and of itself doesn’t sound too terribly bad. But even if you were to simply pay off your attacker, that payment will amount to only about 15% of the total cost of the attack.
What Is Ransomware?
Ransomware is a type of malware that encrypts data. Hackers can use this malware to make an organization’s files completely inaccessible to them unless they pay a ransom (often in cryptocurrency) to get their data back. Some hackers will also threaten to release sensitive information online if the ransom isn’t paid.
Around 63% of ransomware victims choose to pay the ransom, hoping to get back to “normal” as soon as possible to minimize the damage. But that type of thinking is often a big mistake because there is no honor among thieves. Even if you pay, you probably won’t get your data back. In fact, only 26% of organizations that pay get all of their data back as promised. And even if you were to get everything back, paying the ransom doesn’t typically minimize the damage — it can actually double the cost.
Other Ransomware Impacts on Business
It makes sense that most businesses focus solely on recovering their data after an attack happens. But the true cost of a ransomware attack isn’t confined to the ransom.
In addition to any ransomware payment (which I’d recommend against making), you need to consider other possible costs:
- Removing the ransomware from your devices and/or servers
- Downtime
- Lost revenue
- Costs of recreating files
- Replacing hardware or software
- Damage to your reputation
- The likelihood that you’ll be targeted again
- Potential regulatory fines and legal fees
- Identity theft prevention
Will Ransomware Ever Go Away?
I wish I had a better answer, but for the foreseeable future, the answer is no. As cybercrime has now grown more profitable than the drug trade, criminals have become more organized and made cybercrime much easier.
You don’t even have to have any impressive hacking skills to use ransomware — you can simply purchase the software from a criminal who does. Ransomware is easy to use, attacks take very little time to set up, and you can get a lot of money for very little effort. And here’s the real kicker — it’s also relatively easy not to get caught.
How to Help Your Business and Other Small Businesses at Risk for Ransomware
Don’t Pay the Ransom
If ransomware weren’t nearly as profitable, it wouldn’t be nearly as popular among thieves. So one thing you can do to reduce the risk of ransomware for you and for organizations like you is not to pay off a cybercriminal — not ever.
If you need a less altruistic reason, here’s a good one — criminals ( even the dumb ones) understand a good opportunity when they see it. Once they find an organization that 1) doesn’t have good security and 2) will pay a ransom, expect to be targeted again and again and again. And remember, there’s no guarantee you’ll get your data back anyway, even if you pay up.
Strengthen Your Defenses
The other thing you can do is make it much harder for criminals to carry out an attack. And the best way to do that is by following cybersecurity best practices, including providing phishing awareness training for your staff. 90% of ransomware attacks start off as simple phishing scams.
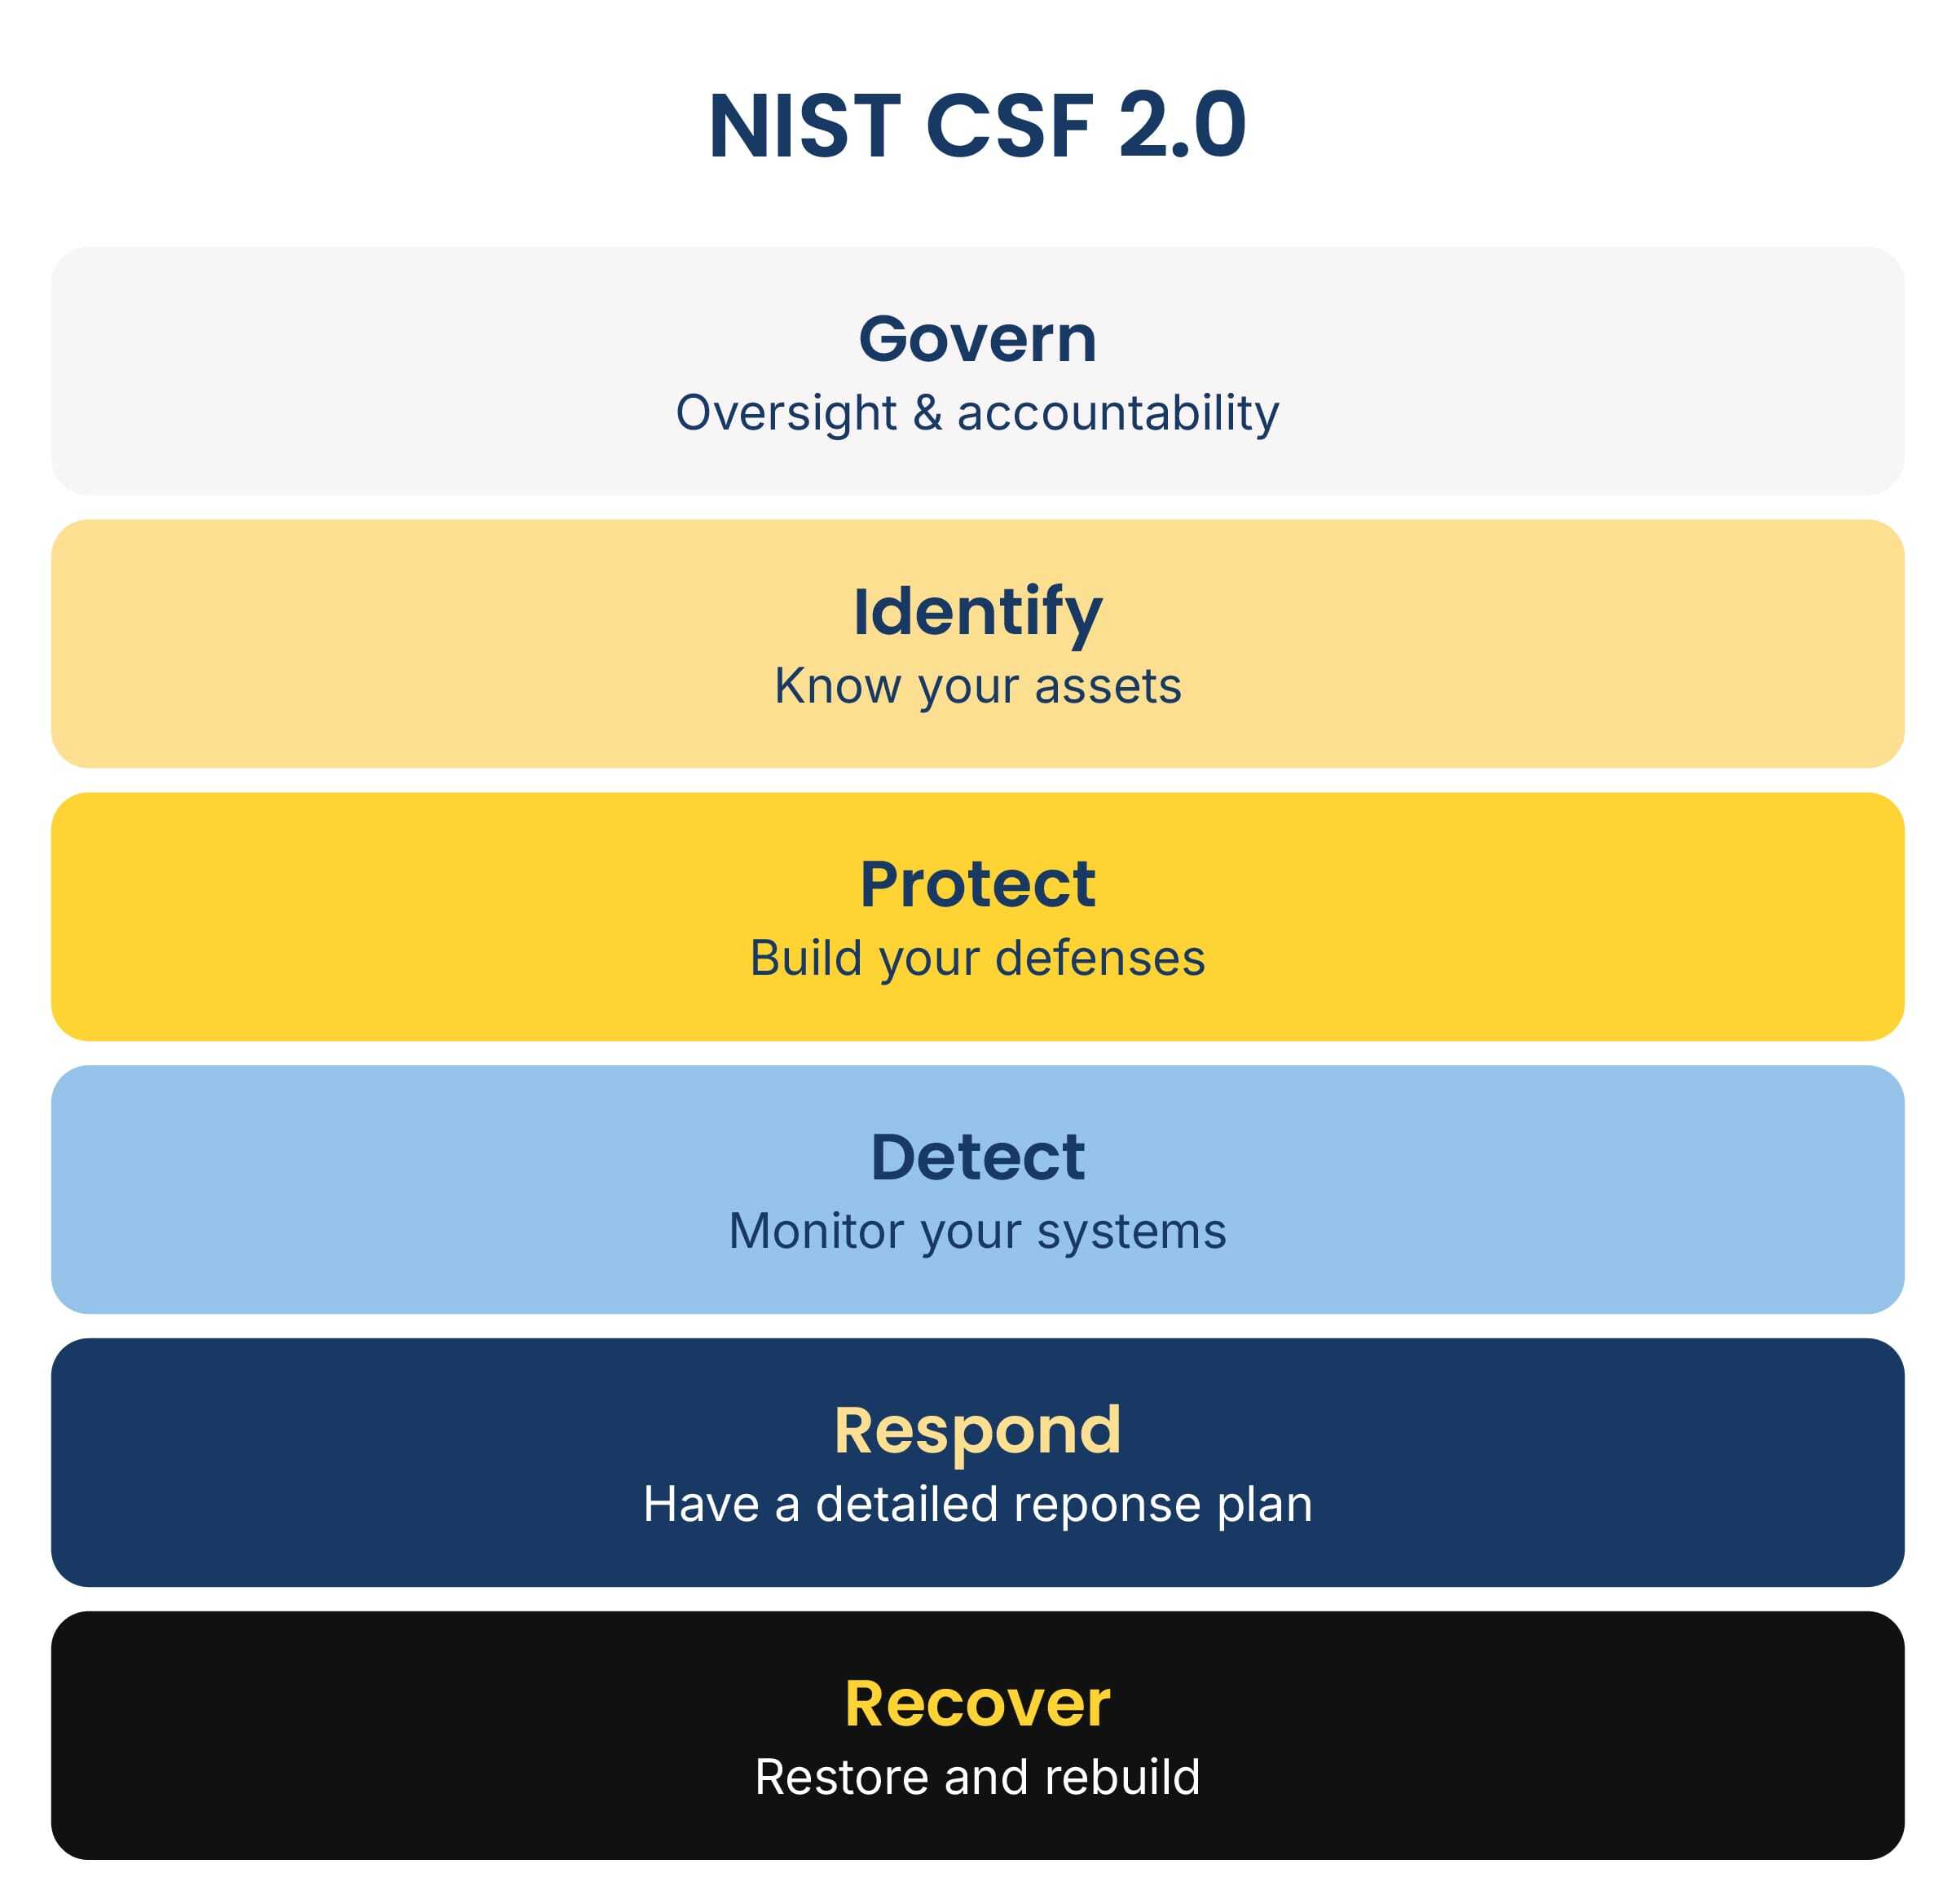
You should also keep your software patched and updated and follow other cybersecurity best practices outlined by institutions like the National Institute of Standards and Technology (NIST).
Backup and Store Your Data Securely
If the worst comes to pass and you are targeted with ransomware, if you have a recent, secure, immutable backup, you can simply refuse to pay and quickly retrieve your data.
Earlier in this blog, I mentioned that some cybercriminals will also threaten to release sensitive data online if ransom is not paid. Data exfiltration — when data is taken or copied for unauthorized purposes — relies on malware. To reduce the threat of data exfiltration, prevent your staff from downloading unauthorized applications, and make sure your network is monitored 24/7 and properly equipped to detect and block unauthorized communication and downloads.
Need Help With Cybersecurity for Small Businesses?
If your IT department is struggling to accommodate remote work or provide timely help desk support, troubleshoot equipment, manage cloud services, and the like, it’s not surprising that duties like keeping software patched and providing ongoing email security training sometimes take a back seat.
Too many organizations don’t start taking cybersecurity seriously until after something bad happens. But recovery can be slow and costly, whereas at Marco, our US-based team of cybersecurity experts can make prevention relatively painless — and it’s exponentially cheaper than an attack.
If you’re worried about your risk for ransomware, you’re not being paranoid. You’re being smart. Feel free to use all of the resources available on our website — including our Small to Midsize Business Cybersecurity Checklist — to help you stay informed about cybersecurity best practices, and if you need help implementing any of them, let us know.