You may have noticed that technology folks speak quickly and use acronyms almost constantly. What can I say? It’s probably all the caffeine. But if you come across a new term now and then, it’s not just you. Cybersecurity is constantly evolving, so even IT pros will run across a new acronym from time to time.
This list of cybersecurity terms includes the terms you’re most likely to hear in 2023. Feel free to bookmark this blog for easy reference, and I’ll try to keep it updated.
Glossary of Cybersecurity-Related Acronyms and Terms
Definitions are based on information from NIST, MITRE, and Gartner.
Advanced Persistent Threat (APT): an adversary, often state-sponsored, which seeks to gain unauthorized access to information technology systems in order to exfiltrate data or to otherwise negatively impact the system.
Business Continuity Plan (BCP): a documented set of instructions or procedures that describe how an organization’s mission and related business processes will be sustained during and after a significant disruption.
Business Email Compromise (BEC): A form of cybercrime that relies on email fraud to attack organizations. 
Business Impact Analysis (BIA): An analysis of an information system’s requirements, functions, and interdependencies used to characterize system contingency requirements and priorities in the event of a significant disruption.
Conditional Access: A set of policies that define and control which devices and users have access to information resources.
Cyber Resiliency: The ability to anticipate, withstand, recover from, and adapt to adverse conditions, stresses, attacks, or compromises on systems that use or are enabled by cyber resources.
Data Loss Prevention (DLP): A system’s ability to identify, monitor, and protect data in use (e.g. endpoint actions), data in motion (e.g. network actions), and data at rest (e.g. data storage). Data loss prevention capabilities are designed to detect and prevent the unauthorized use and transmission of information.
Disaster Recovery Plan (DRP): A written plan for processing critical applications in the event of a major hardware or software failure or destruction of facilities.
Dwell Time: The amount of time a bad actor is inside an organization's network before being discovered.
Endpoint Detection and Response (EDR): A solution that records and stores system-level behaviors and uses data analytics to detect anomalous behavior, provide contextual information, block malicious activity, and provide remediation recommendations to restore affected systems.
Exfiltration: The unauthorized transfer of information from an information system. This may also be known as data exfil, data exportation, data extrusion, data leakage, or data theft.
Intrusion Detection/Prevention System (IDS/IPS): A system that monitors network events into and out of your network, analyzing them for signs of possible incidents and attempting to stop detected possible incidents.
Insider Threat: An entity with authorized access to a system that has the potential to harm, wittingly or unwittingly, an information system or enterprise through destruction, disclosure, modification of data, and/or denial of service.
Indicator of Compromise (IOC): Events, logs, files, or any other pieces of forensic data that indicate potentially malicious activity occurred on a system or network.
Incident Response Plan (IRP): Documentation of a predetermined set of instructions or procedures to detect, respond to, and limit consequences of malicious cyber-attacks against an organization’s information systems.
Information Sharing and Analysis Center (ISAC): An entity created by public or private sector organizations, for purposes of gathering and analyzing critical cyber and related information in order to better understand security problems and interdependencies related to cyber systems, so as to ensure their availability, integrity, and reliability.
Multi-factor authentication (MFA): An authentication system that requires two or more factors for successful authentication. The factors are a combination of something you know, something you have, and something you are.
Penetration Testing: An authorized, simulated test in which evaluators mimic real-world attacks in an attempt to identify ways to circumvent the security features of an application, system, or network.
Phishing: A type of social engineering where an attacker attempts to acquire sensitive data, such as passwords or account numbers, through fraudulent emails or websites.
Protected Health Information (PHI): Individually identifiable health information as defined by the Health Insurance Portability and Accountability Act (HIPAA).
Personally Identifiable Information (PII): Information that can be used to distinguish or trace an individual’s identity, either alone or when combined with other information that is linked or linkable to a specific individual.
Security Operations Center (SOC): Is a centralized team that monitors and responds to security events on an organizational and technical level.
Security Orchestration, Automation, and Response (SOAR): Technologies that enable organizations to collect inputs monitored by the security operations team. This allows for incident analysis and triage to be performed by leveraging a combination of human and machine power to define, prioritize, and standardize incident response activities.
Security Information and Event Management (SIEM): An application that provides the ability to gather security data from information components and present the data as actionable information via a single interface.
Smishing: A type of phishing attack that involve the use of messages sent using the SMS (Short Message Service).
Vishing (voice or VoIP phishing): A type of cyber attack that uses voice and telephony technologies to trick targeted individuals into revealing sensitive data to unauthorized entities.
Additional Help With Cybersecurity
If you’re tasked with providing cybersecurity for a small to midsize business, it can be tough to translate acronyms into action. And what was considered effective cybersecurity just a few years ago is no longer sufficient.
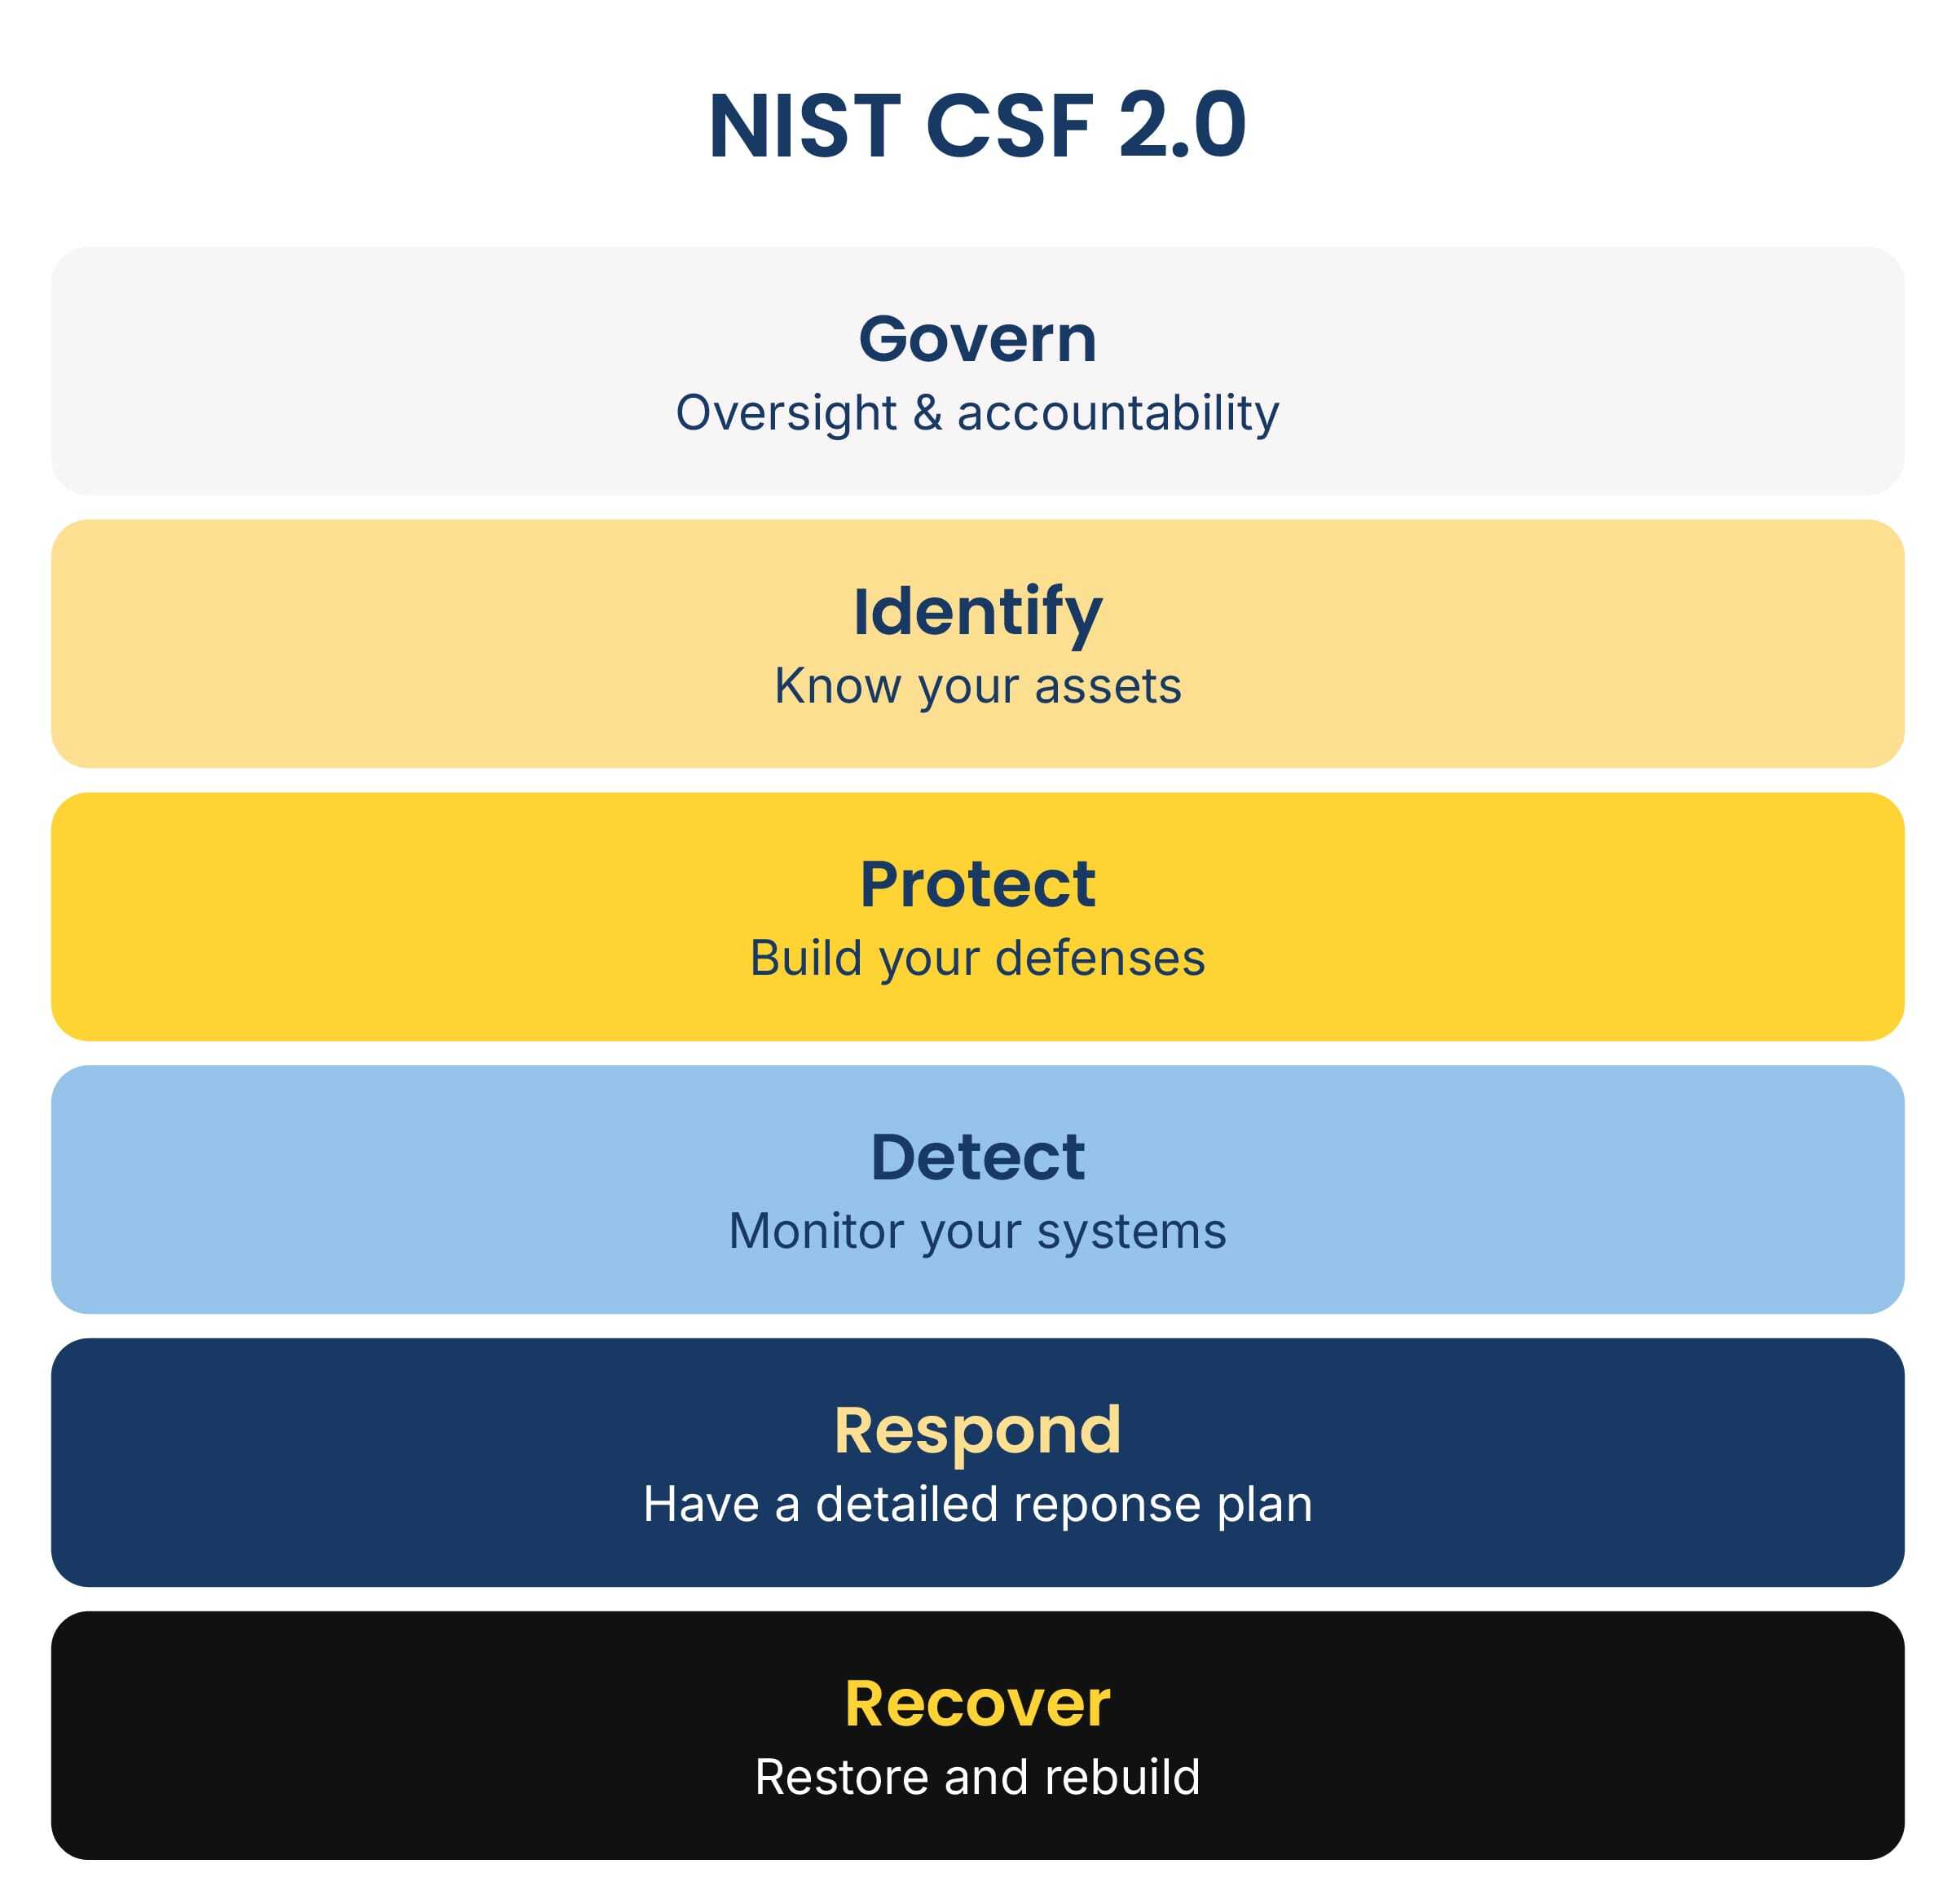
Our cybersecurity team has created an online cybersecurity checklist to help you assess if your SMB is following cybersecurity best practices. And here are a few more acronyms for you: it’s based on current recommendations outlined by the National Institute of Standards and Technology Cybersecurity Framework (NIST CSF) and the Center for Internet Security (CIS). You can complete the checklist online or download a free copy. And if my teammates or I can be of any further help, feel free to reach out!