First off, swatting isn’t anything new, and it has nothing to do with bugs of any kind, let alone the computer variety.
The term “swatting” is, however, related to SWAT (special weapons and tactics) teams, and typically refers to calling in a fictitious emergency. And “swatters” apparently get their thrills by calling in fake bomb threats and other crises, hoping to bait emergency services into sending out a SWAT team. Unfortunately, some of these hoaxes have resulted in death.
What Is Swatting in Cybersecurity?
Unfortunately, it now seems that cybercriminals are starting to explore adapting this technique in a few ways.
C-Suite Attacks
Some cybercriminals mine online bios and the dark web to find detailed information about high-level executives and other stakeholders — typically within the healthcare, biomed, esports, and pharmaceutical industries. They will then use what they find to try to make their “emergency” call more believable.
Extortion and Ransomware
Recently, some cybercriminals are also toying with making swatting pay by adding ransomware and extortion. Here’s how this attack has already played out within the healthcare industry:
1. A cybercriminal will obtain patient records through a data breach
2. They’ll infect a hospital’s network with ransomware
3. They’ll inform the hospital of their intent to use swatting tactics on their patients unless they pay a ransom
The Good and Bad News About Swatting
Thus far, hospitals have chosen to inform local law enforcement of the threat rather than pay the ransom, and so far, that appears to have prevented criminals from successfully swatting their patients. That’s good news, but cybersecurity threats have a tendency to evolve quickly. And unfortunately, there are signs that swatting is going to become a bigger problem.
Some cybercriminals, unsatisfied with their failed attempts to get money from their original target — the hospital — have then contacted individual patients, threatening to release their information on the dark web. And, of course, these criminals may continue to explore more ways to use real-world violence to escalate a cyberattack.
However, whether there’s a cybersecurity component or not, these types of attacks should be on every business’s radar.
Recent Swatting Statistics
Swatting statistics have been difficult to come by, as there is no federal swatting law, and law enforcement doesn’t track these incidents as a distinct category of crime. Swatters are typically prosecuted under other statutes covering fraud, hate crimes, and others.
However, in 2019, the FBI estimated that the annual number of swatting incidents had escalated from 400 in 2011 to over 1,000. And according to a recent survey conducted by the Anti-Defamation League, 11% of teens reported that they had been the target of swatting incidents. And according to Capitol Police, at least 34 US Congress members have been swatted.
Obviously, it can be terrifying for victims to suddenly see a SWAT team assembled outside their homes, and there’s a real possibility that these attacks will lead to more deaths. They also typically cost law enforcement thousands of dollars per incident, although a single incident in New York stuck taxpayers with a $100,000 bill.
How To Prevent Swatting Attacks on Your Business
You can’t prevent someone from making prank calls or making up elaborate emergencies that don’t exist. But that doesn’t mean you’re powerless either.
Here’s what I would tell my clients:
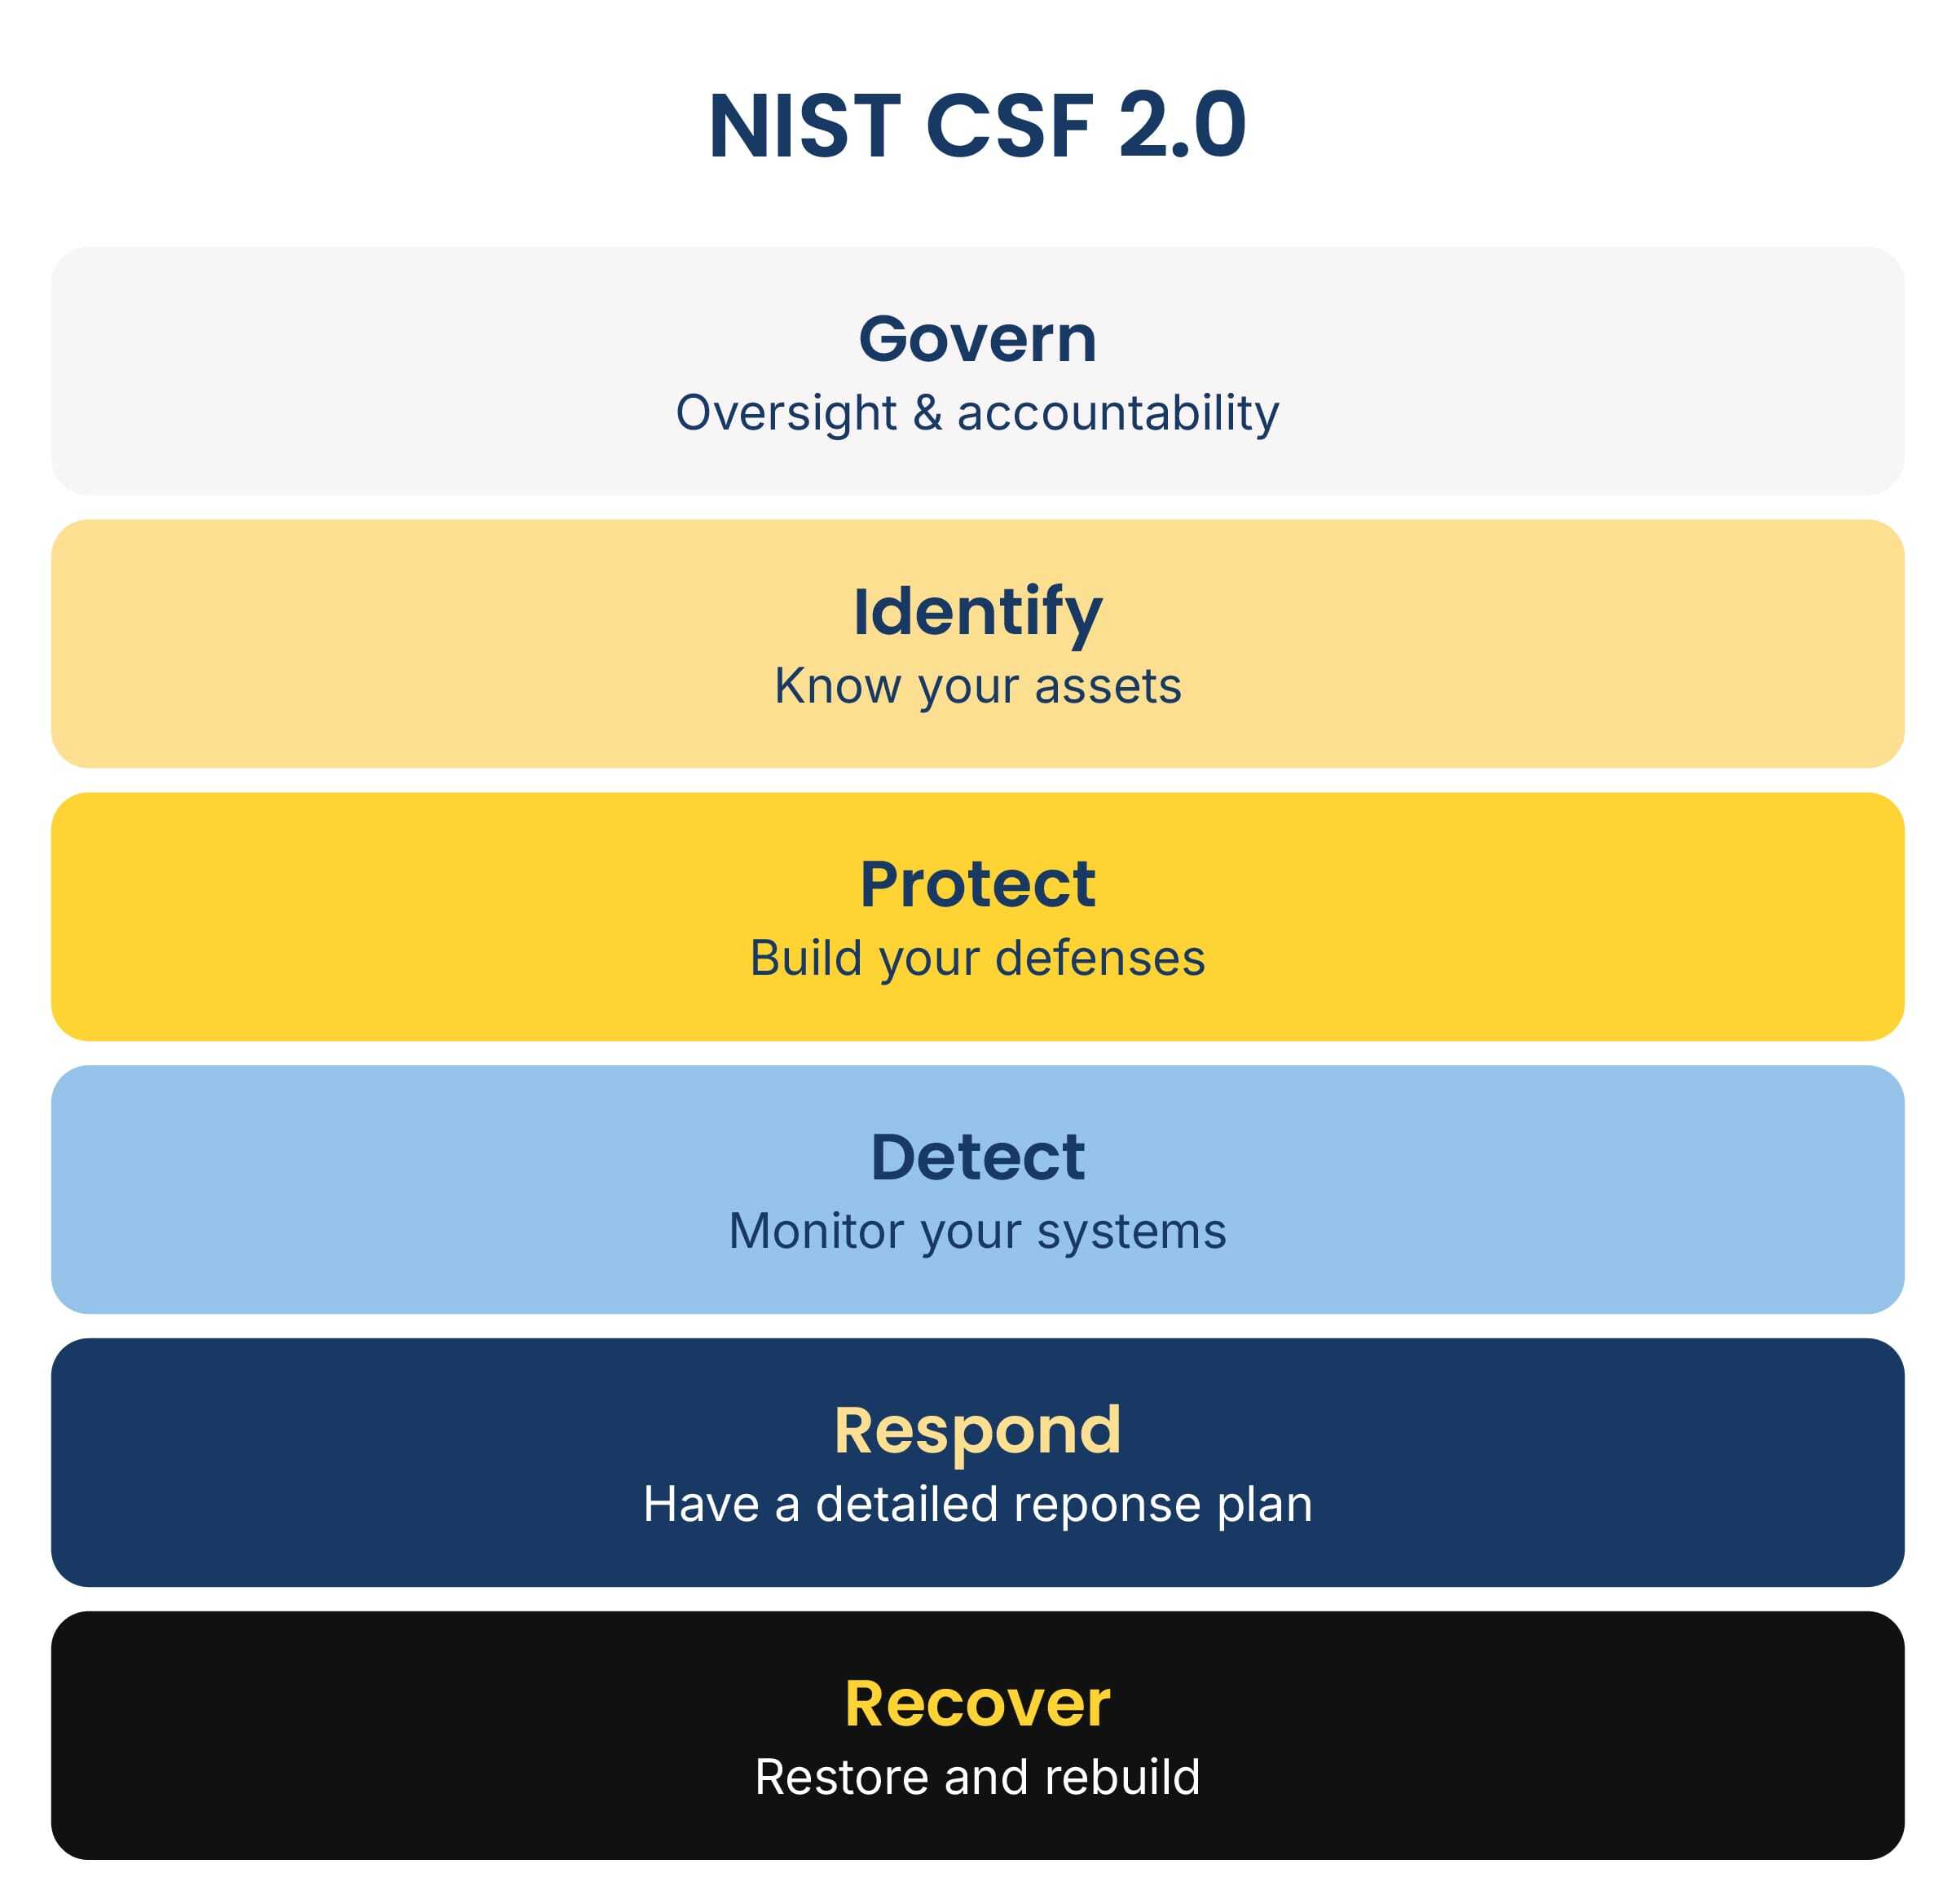
- Make sure you’re following cybersecurity best practices to protect your network and your data
- Train your staff to recognize phishing scams — which are the precursor for 90% of ransomware attacks
- Review the online bios of your executives and other stakeholders, and remove the names of spouses and children or other personal information that could be used to orchestrate a more convincing swatting attack
- If your organization or any staff or board members receive a swatting threat, inform local law enforcement, so that in the event that the attack is carried out, police will proceed with caution
- Don’t pay a ransom — 92% of companies that pay a ransom don’t get all of their data back
Don’t breeze by those first two points. If you haven’t revisited your cybersecurity posture in the past few years, things have changed. And unless your staff is given regular, high-quality security awareness training, in all likelihood, they’re highly susceptible to modern phishing scams.
If you aren’t sure whether your cybersecurity tools and practices would hold up against a hacker, my fellow cybersecurity experts and I created a short quiz. Take my word for it, it’s better to find out you have a few vulnerabilities this way than most others.