At Marco, we spend quite a bit of time talking about cybersecurity disasters. But it’s important to remember that disasters come in many forms, natural and manmade. Technically, a business disaster is anything that disrupts normal operations and could have a serious impact on your finances, your clients, your reputation, and the like.
According to the Federal Emergency Management Agency (FEMA), 40% of organizations don’t reopen following a disaster, and 25% more fail within the same year.
Examples of Common Business Disasters

Business disasters can be caused by many things. Here are just a few examples:
- Severe weather
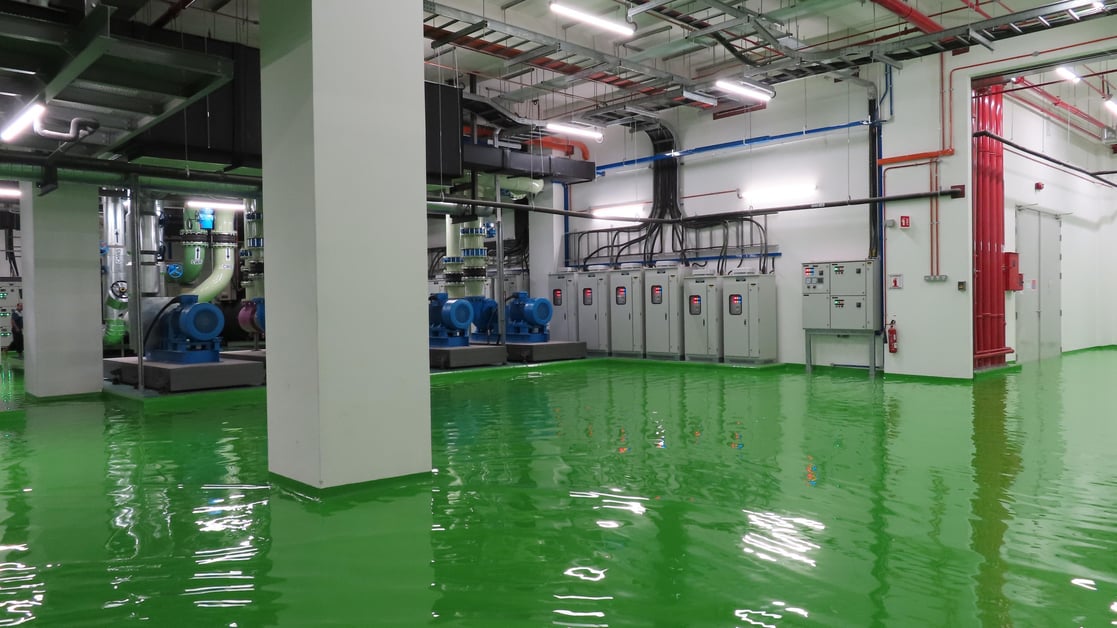
- Workplace fire or flooding
- Cybersecurity incidents
- Legal issues or scandals
- IT emergencies
- Physical security incidents
- Supply-chain disruptions
Disaster Recovery Plans vs. Business Continuity Plans
Disaster recovery and business continuity plans get wrapped up as a single concept. But they are distinctly different and often multi-faceted!
Business continuity focuses on answering the question “How will we continue to be able to operate — and at what capacity — in the wake of a disaster?”
Disaster recovery plans, on the other hand, focus on retrieving your IT resources and data.
You can have a solid disaster recovery plan and still not be able to operate. It’s your business continuity plan that outlines both who and how you will restore operations, as well as what to restore first. . In my experience, organizations don’t fail because they don’t have the data. They fail because they lack business continuity practices.
And in case you were wondering, the very best time to build a business continuity plan is before something bad happens.
5 Steps To Build Your Business Continuity Plan (BCP)

1. Inventory and Rank Applications
Begin by listing all the applications your organization uses to operate and then rank them in order of importance with #1 being the most critical.
Take the time to outline all the applications you use to operate. You likely have far more than you think, so be sure to engage all departments in the process, including IT, security, individual business units, finance, procurement, legal, HR, development, and engineering (if applicable).
Pro tip: This is also a great exercise to discover any tools that serve overlapping purposes and could be streamlined.
2. Identify Your Business-Critical Applications
It is too expensive — and not necessary — to replicate all your applications to ensure access in the case of a disaster.
At Marco, we have over 150 applications we use for varying purposes, but we have identified 5 as essential to continuing minimal operations.
Identify the apps that are absolutely necessary to function at a baseline level, and think through how you will make sure they are accessible. Fortunately, the rise of cloud computing is making accessibility relatively simple — even after something as devastating as a fire.
3. Outline Regular Tasks
Map out the tasks you will be able to complete — or not — during a disaster. Break down each process into specific steps. Then determine what steps can be done remotely, which ones would need an alternate site, which ones would not be possible, and how long the business can function if they are not completed.
For each possible task, identify a person (and a backup) that is responsible for doing the task in the case of an emergency.
4. Assign Mission-Critical Roles
Identify who will continue working and where, and map out a decision tree. In most cases, many employees will be sent home. If your office doesn’t typically accommodate remote or hybrid work, make sure your employment policies outline how you would handle these circumstances.
Pro tip: Don’t neglect the importance of solid communication! It’s vital to preserve the trust of your employees, suppliers, business partners, vendors, and other stakeholders by informing them of what happened, what your next steps are, and what they can expect.
Some businesses also have a separate disaster recovery communication plan.
5. Map Out More Likely Scenarios
What significant business disruptions are more likely to impact your organization internally and externally? Internal disruptions affect only your organization’s ability to communicate and do business (i.e. building issues). External disruptions relate to natural disasters, power outages, or criminal attacks.
Go deeper to think through scenarios at each of your locations.
An outage at your organization’s main office, for example, will have different implications for other offices, and the steps you take afterward will look different. For example, if your main office goes offline, would employees be able to access other locations?
Additional Disaster Preparation Tips
In addition to a formal written business continuity plan, here’s what I would advise:
- Keep emergency supplies, like a flashlight, a first-aid kit, drinking water, and other emergency supplies at your location
- If it would be very difficult for your business to function at another location, consider a generator and other equipment that could preserve critical operations should you lose power
- Maintain more than one backup of your data, and store a copy of critical documents — like insurance policies, financial information, important contact information, and a copy of your BCP and DR plans — offsite
- Test your business continuity plan and your backups to make sure you can rely on them in an emergency
Physical Workplace Disaster Response and Recovery Tips

People don’t always think clearly after a disaster. If you already have a disaster recovery plan and a business continuity plan, follow those closely. Around 46% of organizations don’t have a disaster recovery plan in place. If yours is one of them, here are some ways to make sure one disaster doesn’t create others:
- Don’t enter your workplace unless it is safe to do so
- Make sure entry points to your building are only accessible by authorized personnel
- Secure any valuable equipment and sensitive data
- Document the damages, including photos and videos
- Use tarps or make other temporary repairs to minimize additional damage
- Contact your insurer to initiate a claim, and keep any related receipts
Backup and Disaster Recovery Services
We do offer backup and disaster recovery services, but we would always rather help an organization prevent something terrible from happening.
Many of our clients find our Backup as a Service (BaaS) plan gives them the peace of mind they need. We can protect your business data and applications by storing them securely off-site — whether in the cloud, at a remote location, or both. However, this service goes beyond simple storage. At Marco, this service also includes a plan for inbound and outbound calls and enabling remote work, so your business can preserve essential operations.
Click the link below to learn more!